EMA Research –Only 33% of enterprises enforce AI agent least privilege access
Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.
BlogContact Us
Cequence Security
Financial Services
2023-predictions-staying-one-step-ahead-in-api-protection,api-security-2024-predictions,api-security-financial-services,api-security-lacking-for-ecosystem-and-third-party-apis,api-security-breaches,cfpb-announces-major-open-banking-proposed-rule,ffiec-api-security-guidance,financial-aggregators-a-vehicle-for-credential-exploitation,financial-services-api-protection,financial-services-customer-stops-millions-of-api-based-account-takeover-attacks-ato,guest-blog-api-security-off-to-a-booming-start-but-were-not-done-yet,reaching-a-tipping-point-in-identity-verification,regulations-and-standards-drive-need-for-api-security,revised-payment-services-directive-psd2,shield-right-while-shifting-left-to-eliminate-fdx-api-security-gaps-at-runtime,tales-from-the-front-lines-protecting-financial-services-mobile-application-apis-from-automated-attacks,the-open-banking-api-security-imperative,unpacking-the-new-cfpb-rule-on-open-banking
financial-services
Current Events
api-breach-duolingo,api-security-need-to-know-lessons-learned-from-the-peloton-security-incident,disney-account-takeovers-how-the-information-is-used-2
current-events
Industry Reports
api-layer-attacks-2026-dbir,best-in-class-api-security,dbir-api-security,new-api-threat-research-shows-that-shadow-apis-are-the-top-threat-vector,survey-highlights-api-business-value-and-api-security-balancing-act,verizon-2025-dbir-review,verizon-dbir-insights,when-does-comparison-shopping-become-malicious
industry-reports
OWASP
2023-predictions-staying-one-step-ahead-in-api-protection,api-breach-duolingo,api-protection-and-cloud-native-application-protection-platforms-cnapp,api-security-financial-services,api-security-meets-government-regulators,api-security-need-to-know-top-5-authentication-pitfalls,api-security101,api-security-breaches,cfpb-announces-major-open-banking-proposed-rule,connected-car-safety-and-api-security,evolution-of-owasp-api-top-10,owasp-api-risks-cant-be-blocked-but-can-be-fixed,owasp-api-vulnerabilities-exploited-to-bypass-api-security,tales-from-the-front-lines-how-third-party-apis-simplify-enumeration-attacks,top-7-selection-criteria-for-automated-bot-prevention-solutions,unpacking-the-new-cfpb-rule-on-open-banking,zero-trust-api-security-model
owasp
Product News
a-winning-trifecta-api-gateways-api-security-and-api-protection,advance-your-api-security-with-amazon-api-gateway-api-sentinel,ai-agent-prompt-injection-credential-theft,api-protection-in-heterogeneous-environments,application-security-in-kubernetes-why-we-joined-cncf,cequence-achieves-pci-dss-3-2-and-soc-2-compliance,cequence-end-of-year-product-recap-strengthening-your-api-security,cequence-security-awarded-best-enterprise-cybersecurity-solution-of-the-year,cequence-securitys-unified-api-protection-solution-wins-three-2023-globee-awards,cequence-unified-api-protection-wins-2023-cyber-top-20-award,cequence-api-security-and-hpe-greenlake,complete-api-security-coverage-with-proxy-and-service-mesh-integration,complete-api-security-with-cequence-uap-and-cdn-integrations,groundbreaking-api-security-generative-ai,sinet16-innovators-award-validates-api-security-and-bot-management-belong-together
cequence-product-news
CQ Prime Threat Research
a-defenders-view-of-log4j-in-automated-attacks,anatomy-of-a-retail-shopping-bot,api-security-need-to-know-excessive-data-exposure,api-threat-research-validates-robust-api-security,bot-as-a-service-the-consumerization-of-botting,cequence-blocks-credential-stuffing-attack,fake-account-creation-its-fraud-by-any-other-name,heres-why-javascript-based-bot-detection-doesnt-work-is-your-site-listed-here,hidden-dangers-of-untrusted-mcp-servers,how-this-cool-sneakerhead-mom-beat-the-bots,long4j,long4j-findings-confirm-log4j-vulnerability-patching-gaps,moving-from-threat-hunting-to-threat-catching,multi-tenant-saas-authentication-bypass-or-works-as-designed,network-iq-how-the-largest-api-threat-database-protects-your-apis,new-api-research-shows-62-growth-in-atos-targeting-login-apis,new-report-big-breaches-breed-bad-bots,reality-check-automated-shopping-bots-are-a-business-problem,romance-scams-plague-dating-apps,state-of-api-security-activity,the-api-security-conversation-that-the-verizon-data-breach-report-missed,what-are-api-keys-and-why-do-i-need-api-key-security
cq-prime-threat-research
About Cequence
3-steps-to-shielding-right-while-shifting-left-for-api-protection,agentic-ai-monetization,are-api-threat-protection-and-bot-management-related,cequence-achieves-aws-security-competency-status,cequence-announces-ml-based-security-enhancements,cequence-security-awarded-best-enterprise-cybersecurity-solution-of-the-year,cequence-security-named-a-2021-tag-cyber-distinguished-vendor,cequence-securitys-unified-api-protection-solution-wins-three-2023-globee-awards,cequence-unified-api-protection-wins-2023-cyber-top-20-award,cfpb-announces-major-open-banking-proposed-rule,comprehensive-api-protection,enabling-retail-deals-and-repelling-the-steals,ffiec-api-security-guidance,guest-blog-api-security-off-to-a-booming-start-but-were-not-done-yet,hand-sanitizer-samples-face-masks-and-api-security-an-rsa-2020-recap,industry-recognition-for-api-sentinel-kuppingercole,javascript-injection-good-for-fraud-detection-bad-for-security-2,making-a-build-vs-buy-bot-prevention-decision,organizations-are-changing-application-security-must-change-too,predictions-2021-getting-an-edge-against-the-bots,prep-the-halls-readying-your-retail-environment-for-the-holiday-rush,reaching-a-tipping-point-in-identity-verification,rsa-conference-2023-api-security,safeguarding-financial-health-why-cfos-should-prioritize-api-security,shield-right-while-shifting-left-to-eliminate-fdx-api-security-gaps-at-runtime,sinet16-innovators-award-validates-api-security-and-bot-management-belong-together,some-recent-api-security-related-gaffes-and-how-they-might-have-been-avoided,ten-things-your-api-security-solution-must-do-part-i,ten-things-your-api-security-solution-must-do-part-ii,the-analyst-perspective-observations-from-cequences-2021-api-specification-survey,unified-api-protection,unpacking-the-new-cfpb-rule-on-open-banking,what-happens-when-your-entire-company-learns-ai-together-we-found-out,why-do-i-need-api-security-if-i-have-a-waf-and-api-gateway,why-unified-api-protection
about-cequence
Customer Case Studies
api-security-case-study,application-security-solving-the-hardest-problem-first,balancing-bot-detection-with-customer-experience,cequence-unified-api-protection-squashes-phishing-campaign-in-a-matter-of-hours-time-to-value,customer-story-zoosk-security,financial-aggregators-a-vehicle-for-credential-exploitation,flash-sales-and-sneaker-drops,gift-card-and-loyalty-program-abuse,poshmark-api-protection-case-study,sms-pumping-fraud,tales-from-the-front-lines-protecting-financial-services-mobile-application-apis-from-automated-attacks,tales-from-the-front-lines-retail-customer-stops-200k-gift-card-fraud-scheme
customer-case-studies
API Security
2026-verizon-dbir-bots-web-app-attacks-agentic-ai,a-year-in-review-in-one-word-momentum,agentic-ai-application-protection-platform-waap,announcing-api-sentinel,announcing-cequence-waap,announcing-general-availability-of-cequence-api-sentinel-2-0,announcing-unified-api-protection-v2-0,api-layer-attacks-2026-dbir,api-security-api10-defined-as-bots-abusing-well-formed-apis,api-security-lacking-for-ecosystem-and-third-party-apis,api-security-need-to-know-lessons-learned-from-the-peloton-security-incident,api-security-threat-research-retail-holiday-report-2023,app-instrumentation,attack-detection-and-threat-hunting-common-topics,automating-attacks-with-chatgpt,better-bot-management,bola-attack-protection-telecom,business-logic-abuse,canadas-largest-retail-pizza-chain-moves-from-reactive-to-proactive-api-protection-with-cequence,cequence-achieves-pci-dss-3-2-and-soc-2-compliance,cequence-and-software-ag-partner-to-deliver-end-to-end-api-security,cequence-api-security-at-black-hat-2024,cequence-end-of-year-product-recap-strengthening-your-api-security,cequence-named-to-cyber-66-list,cequence-q4fy26-momentum-agentic-ai-security,cequence-security-makes-its-rsa-debut-2,cequence-unified-api-protection-squashes-phishing-campaign-in-a-matter-of-hours-time-to-value,cequence-api-security-and-hpe-greenlake,chatgpt-for-api-security,comprehensive-api-protection,discover-public-api-attack-surface-with-new-api-spyder,end-to-end-api-security,financial-services-api-protection,gartner-recognition-when-it-rains-it-pours,gift-card-and-loyalty-program-abuse,hey-api-what-you-token,how-a-broken-object-level-authorization-vulnerability-exposed-sensitive-data-api-security-report,how-automated-api-attacks-are-the-digital-equivalent-of-mockingbirds,how-bola-leads-to-enumeration-and-ato-attacks,idor-vulnerability,introducing-api-bites-from-cequence-security,iocs-in-your-apis,kasa-camera-vulnerability-discovery,leading-telecom-slashed-account-takeovers,looking-for-a-silver-tail-replacement,mergers-and-acquisitions-in-api-security-and-bot-management,new-api-threat-research-shows-that-shadow-apis-are-the-top-threat-vector,owasp-api-security-top-10-a-framework-for-improving-your-api-security-efforts,owasp-api-security-top-10-from-a-real-world-perspective,owasp-api-vulnerabilities-exploited-to-bypass-api-security,owasp-appsec-training-day-api-attacks-beyond-the-owasp-api-top-10,owasp-top-10-lists-end-state-or-starting-point,prying-eye-vulnerability-direct-to-api-enumeration-attack-enables-snooping,regulations-and-standards-drive-need-for-api-security,tales-from-the-front-lines-attackers-on-lockdown-focus-on-apis,tales-from-the-front-lines-attackers-target-apis-with-get-based-atos,tales-from-the-front-lines-protecting-financial-services-mobile-application-apis-from-automated-attacks,tales-from-the-frontlines-api-sentinel-drives-security-collaboration,the-cequence-security-blog-top-5-posts-of-2020,the-danger-of-web-scraping-and-how-to-prevent-it,ulta-beauty-reduces-costs-by-blocking-api-based-enumeration-attacks,unified-api-protection-7-3,unified-api-protection-for-telcos-customer-testimonial,unified-api-protection-recognized-kuppingercole,whats-new-cequence-api-security-platform-further-advances-end-to-end-vulnerability-and-automated-attack-mitigation,whats-new-cequence-unified-api-protection-siem-integration
api-security
Bot Management
2022-predictions-protecting-an-api-centric-world,2025-api-security-predictions,2026-verizon-dbir-bots-web-app-attacks-agentic-ai,a-defenders-view-of-log4j-in-automated-attacks,agentic-ai-api-security,agentic-ai-application-protection-platform-waap,agentic-ai-security-behavioral-analysis,ai-agents-are-bots-api-defense,analysis-preventing-fake-account-creation-and-romance-scams-2,announcing-cequence-waap,api-0day-response-a-moveit-story,api-breach-duolingo,api-layer-attacks-2026-dbir,api-protection-and-cloud-native-application-protection-platforms-cnapp,api-protection-in-heterogeneous-environments,api-protection-in-telecommunication-protected-in-less-than-30-minutes,api-security-2024-predictions,api-security-api10-defined-as-bots-abusing-well-formed-apis,api-security-in-your-operational-technology-ot,api-security-lacking-for-ecosystem-and-third-party-apis,api-security-podcast-how-apis-enable-digital-transformation-and-automated-attacks,api-security-threat-research-retail-holiday-report-2023,api-threat-detection,api-threat-prevention,api-threat-research-validates-robust-api-security,are-api-threat-protection-and-bot-management-related,are-these-13-scary-security-gaps-in-your-apis,automating-api-security,aws-vpc-traffic-mirroring-integration-coming-soon-2,beyond-magecart-understanding-the-risks-and-impacts-of-third-party-javascript,block-api-attacks,bot-attacks-one-week-in-the-life-of-a-customer,bulletproof-proxies-the-evolving-cybercriminal-infrastructure,bulletproof-proxy-market-update,business-impacts-of-api-security-breaches,canadas-largest-retail-pizza-chain-moves-from-reactive-to-proactive-api-protection-with-cequence,cequence-security-awarded-best-enterprise-cybersecurity-solution-of-the-year,cequence-securitys-unified-api-protection-solution-wins-three-2023-globee-awards,cequence-unified-api-protection-wins-2023-cyber-top-20-award,creating-credential-stuffing-resistant-applications,dbir-api-security,disney-account-takeovers-how-the-information-is-used-2,ffiec-api-security-guidance,financial-services-api-protection,forrester-bot-management-wave-2022,fortune-500-retailer-saves-1-7-million-by-eliminating-account-take-overs-2,heres-why-online-holiday-inventory-is-often-gone-before-you-get-there-3,how-shadow-apis-simplify-automated-attacks,implementing-a-dynamic-sampling-strategy-in-spark-streaming,industry-recognition-for-runtime-application-security-omdia-research,introducing-cq-prime-the-cequence-security-threat-research-team,moving-fast-without-api-guardrails,old-habits-die-hard-industrial-controls-credential-sharing-and-password-spraying,pci-dss-4-compliance-api-security,poshmark-api-protection-case-study,rsocks-takedown,simplifying-bot-prevention-with-cdn-integration,sinet16-innovators-award-validates-api-security-and-bot-management-belong-together,state-of-api-security-activity,survey-highlights-api-business-value-and-api-security-balancing-act,tales-from-the-front-lines-a-long-weekend-ruined-for-whom-2,tales-from-the-front-lines-attackers-on-lockdown-focus-on-apis,tales-from-the-front-lines-attackers-target-apis-with-get-based-atos,tales-from-the-front-lines-how-third-party-apis-simplify-enumeration-attacks,tales-from-the-front-lines-large-retailer-achieves-near-immediate-time-to-value,tales-from-the-front-lines-maintaining-detection-efficacy-and-your-cool-in-the-summer-heat,tales-from-the-front-lines-protected-in-just-33-minutes,tales-from-the-front-lines-retailer-prepares-for-holiday-bot-battle-in-a-matter-of-weeks,tales-from-the-front-lines-why-simple-attacks-like-content-scraping-are-the-hardest-to-block,tales-from-the-frontlines-increasingly-sophisticated-cat-and-mouse-games,ten-things-your-api-security-solution-must-do-part-ii,the-critical-role-real-time-protection-plays-in-api-security,the-rise-fall-of-single-request-bots-2,threat-advisory-recent-high-volume-bot-traffic-from-ipvanish-vpn-against-retailers,unified-api-protection,unified-api-protection-7-3,using-an-api-security-checklist-what-should-you-look-for,verifiable-ai-agent-identification,verizon-dbir-insights,what-are-fake-accounts-and-how-can-they-be-worth-44-billion,what-is-account-takeover-ato,what-is-api-threat-detection,what-is-api-threat-mitigation,what-sets-cequence-apart-from-anyone-else,why-unified-api-protection,your-bot-problem-may-be-an-api-problem
bot-management
AI
2026-verizon-dbir-bots-web-app-attacks-agentic-ai,agentic-ai-api-security,agentic-ai-monetization,agentic-commerce-bot-defense,ai-gateway-introduction,automating-attacks-with-chatgpt,beyond-captcha-biometric-verification-bot-detection,bot-defense-pricing-success-penalty,chatgpt-for-api-security,the-genai-gold-rush
ai

Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.

FEATURED BLOG

AI Security Blog

Introducing Agent Trust: Managing Agents with Identity Plus Behavior

AI agent identity verification proves who an agent is. Agent Trust adds behavioral analysis so security teams can govern what it does.
Read More
Introducing Agent Trust: Managing Agents with Identity Plus Behavior
Laptop with a phone and a credit card representing retail cybersecurity
API Security

Weathering Retail Cybersecurity Storms

October 29, 2024

7

Read Blog
The retail industry is highly seasonal, experiencing tremendous activity bursts during specific periods. Many of these periods coincide with holidays like Memorial Day, Labor Day, and Christmas with retailers launching grand promotions that result in frenzied activity in both their physical and electronic storefronts. Major retailers now see levels of revenue from their e-commerce engines […]
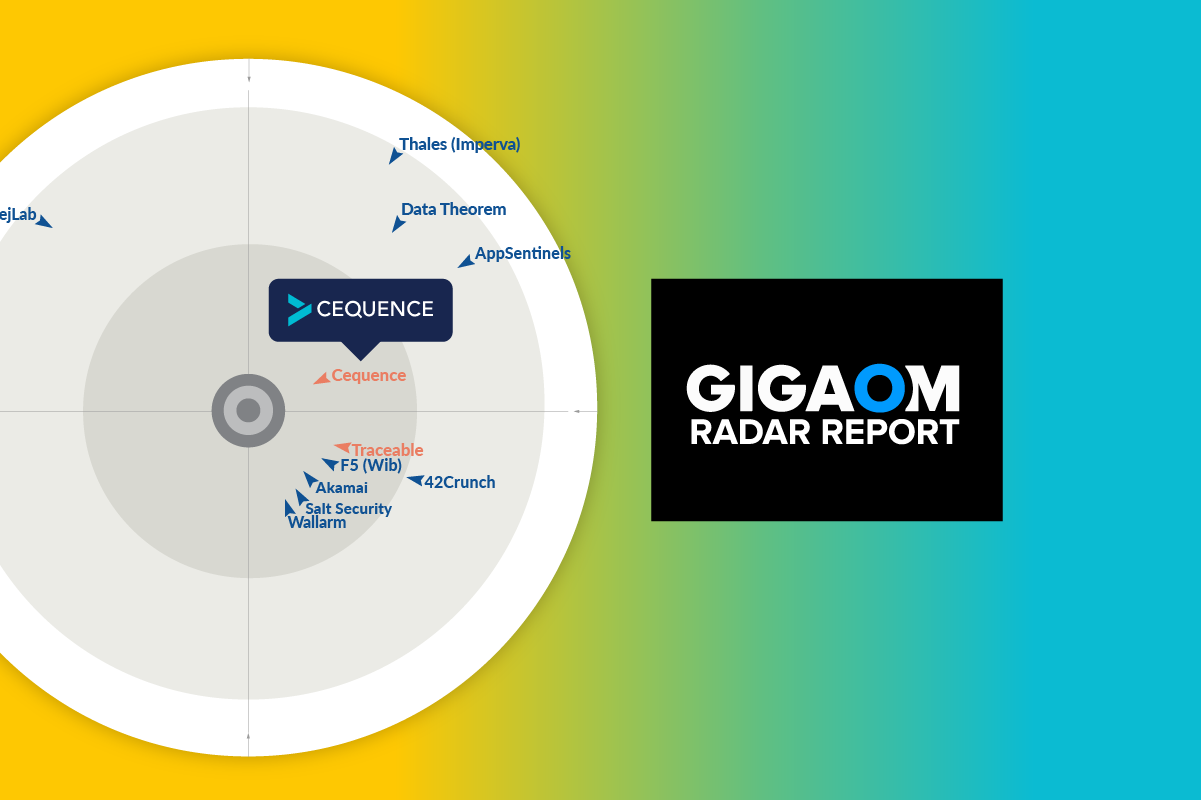
Cequence Security a Leader and Outperformer in GigaOm API Security Radar Report
API Security

Cequence Security – A Leader and Outperformer in GigaOm API Security Radar Report

October 25, 2024

4

Read Blog
Cequence Security has been recognized as a Leader and Outperformer in the new GigaOm Radar for API Security report, highlighting our innovative approach and comprehensive protection capabilities. This recognition comes as a testament to our dedication to safeguarding digital assets in an increasingly complex software landscape. The GigaOm report specifically praises the Cequence Unified API […]
What is DORA (Digital Operational Resilience Act) compliance
Financial Services

What is DORA (Digital Operational Resilience Act)?

October 17, 2024

5

Read Blog
The Digital Operational Resilience Act (DORA) is a significant regulation introduced by the European Union, set to take effect on 17 January 2025. While DORA is primarily designed to enhance the operational resilience of financial entities against ICT-related incidents, its impact extends far beyond financial institutions. DORA establishes requirements and principles that financial entities must […]
Cequence Trust Center: Commitment to Security and Compliance
About Cequence

Cequence Trust Center: Commitment to Security and Compliance for Our Customers

October 15, 2024

4

Read Blog
Why Trust Centers Matter A Trust Center plays a crucial role in building and maintaining trust with customers. It provides a single source of truth for security documentation, certifications, and ongoing updates, helping businesses reassure customers that their data is in safe hands. Trust Centers streamline security review processes, reduce the need for repetitive communications, […]
A stylized picture of a laptop with a sneaker on it and a credit card implying a purchase representing a flash sale sneaker drop
Bot Management

Flash Sales, Sneaker Drops, and Concert Tickets: Protecting Your Applications, APIs, and Bottom Line

October 10, 2024

4

Read Blog
Flash sales, hype sales, and online product launches – like limited-edition sneakers – generate interest, excitement, and high demand from customers, so naturally they have also become a target for cyberattacks. These events often involve high-value items, making them prime targets for malicious actors and their bot armies. Understanding application and API vulnerabilities and the […]
Stylized image of a bandage patching a separation between two panels representing virtual patching
API Security

Virtual Patching: A Proactive Approach to API Security

October 3, 2024

6

Read Blog
In the API-driven world of modern enterprises, security vulnerabilities such as Broken Object Level Authorization (BOLA) represent one of the more insidious threats. These weaknesses are often exploited by attackers through bot-driven automation and can lead to data breaches and privacy violations. It’s not always convenient or even possible to immediately remediate the problem through […]
Stylized image of a phone, coins, and an electric car charging representing GenAI
API Security

GenAI and the Gig Economy: Protecting Against GenAI Threats

September 26, 2024

7

Read Blog
The Rise of the Gig Economy and GenAI The gig economy, driven by short-term contracts and freelance work, has dramatically reshaped the modern business landscape. Popular platforms such as Uber, Lyft, and Fiverr enable seamless interactions between users, gig workers, and service providers through the power of APIs. These APIs are critical to providing real-time […]
Travel Cybersecurity and Hospitality Security During Peak Seasons
CQ Prime Threat Research

Hospitality & Travel Cybersecurity: Protection During Peak Seasons

September 17, 2024

4

Read Blog
Travel and hospitality companies are entering one of the busiest times of the year, with peak seasons like vacations and holidays bringing a surge in traveler activity. Unfortunately, this increase in traffic also attracts cybercriminals, who exploit the high volume of online activity to launch attacks. For travelers, this means being extra cautious with personal […]
Stylized stars appear to be moving across the image from left to right representing the GenAI gold rush
Bot Management

The GenAI Gold Rush – Securing Gen AI While Moving Fast

September 12, 2024

4

Read Blog
All technological disruptions of the past three decades have exhibited a similar trait wherein security took a backseat to innovation, and generative AI (GenAI) has been no exception. While enterprises and consumers are rushing to embrace this new disruptive technology, security is simply not top of mind for most of them. As such, there are […]
API security and application security case study – Hibbett
API Security

API Security Drives Business Growth for Hibbett

September 10, 2024

4

Read Blog
Protecting Hibbett’s Future (and Past) with API Security The mark of many successful businesses is longevity, and Hibbett certainly fits that description. They have been around longer than many, if not most, retailers in the U.S. Headquartered in Birmingham, Alabama and established in 1945, the retailer has successfully distinguished itself from others by building a […]
Cequence Protects Against BOLA Attacks
Bot Management

Cequence Protects 6 Major Telecoms from BOLA API Attacks

September 5, 2024

6

Read Blog
Cequence recently protected multiple major telecommunications companies, each a global leader with over 100 million customers, from a series of six high-profile Broken Object Level Authorization (BOLA) API attacks. Most of these companies use Google’s Apigee API Gateway and rely on Cequence for advanced threat detection and prevention. Cequence successfully blocked over 22 million malicious […]
A stylized image of a card with a bow on it and copies of that card with a warning sign on them going off into the distance representing gift card and loyalty program abuse
Bot Management

What is Gift Card and Loyalty Program Abuse?

August 29, 2024

4

Read Blog
Gift cards and loyalty programs are used by retailers to increase customer traffic, build brand awareness, and gain new customers. However, they also attract the attention of fraudsters who exploit these systems, causing substantial financial losses and undermining customer trust. This blog explores the nature of gift card and loyalty program abuse and how proper […]
Join our API Security Bootcamp
About Cequence

Unleashing the Power of API Security: Join Our API Bites Bootcamp Series

August 20, 2024

2

Read Blog
API Security: A 2024 Initiative for All Organizations In the rapidly evolving digital landscape, API security has emerged as a top priority for organizations of all sizes. Protecting your APIs is not just about defense; it’s about staying ahead of potential threats and ensuring the seamless operation of your applications. That’s why we’re excited to […]
API discovery tool, API security
API Security

Ensuring High-Efficacy Zero-Knowledge API Discovery

August 15, 2024

4

Read Blog
Most organizations do not have an accurate estimate of their API footprints – and why would they? With the rate at which APIs are getting churned out or updated, it’s a significant challenge for an InfoSec organization or a SOC team to be aware of, let alone up to date on, all the APIs that […]
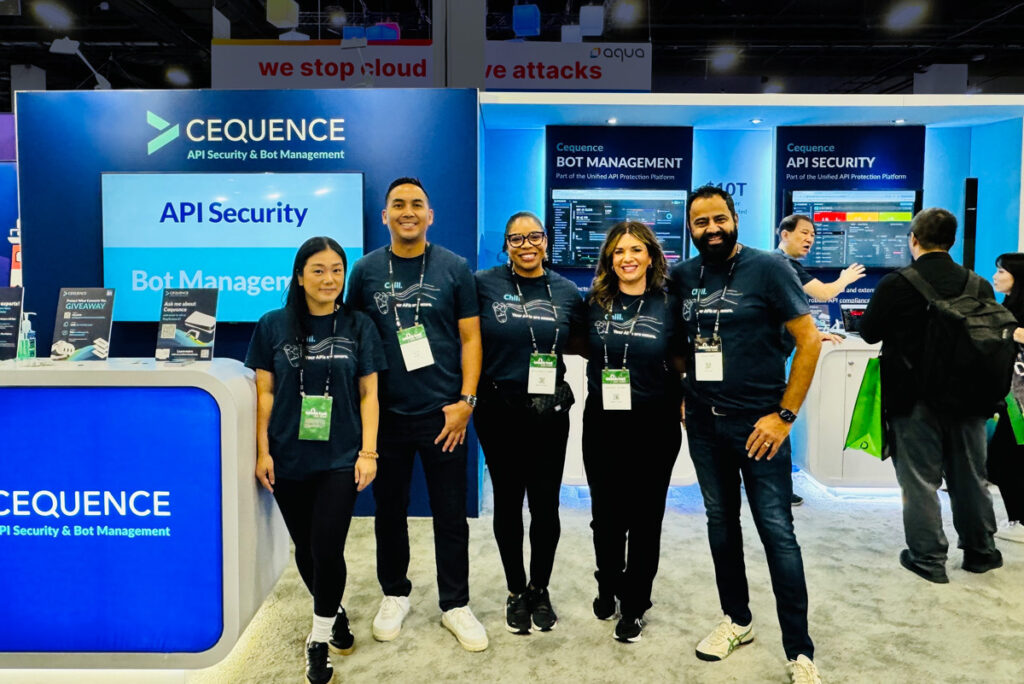
A photo of the Cequence booth staff in front of the futuristic-looking Cequence trade show booth at the Black Hat 2024 conference.
About Cequence

Cequence Storms Black Hat with API Security Testing for Generative AI Applications

August 13, 2024

2

Read Blog
That’s a wrap for Black Hat 2024! We had a great show and met many of you at the booth or on the show floor. I hope you were able to come by, watched a session by Jason Kent, Hacker in Residence at Cequence, or Parth Shukla, Security Engineer at Cequence, and maybe even entered […]
Unified API Protection (UAP) v7.3 - api security, summary dashbaord, api inventory, ai bot detection and attack surface detection
Product News

Advancing API Security and Bot Management with Cequence UAP v7.3

August 8, 2024

4

Read Blog
Cequence is excited to announce the latest release of our Unified API Protection (UAP) platform, version 7.3. This release has big new features and updates to existing capabilities, so let’s take a tour. The major feature categories include: New Summary Dashboard New API Inventory Page New Integrations New ML-based Threat Classification Automated AI Bot Detection […]
AI attack surface, api compliance, api attack surface, discover api attack surface, secure api attack surface
API Security

It’s 11:30 pm, do you know what AI your apps are hanging out with?

August 6, 2024

5

Read Blog
Digital Transformation and Expanded AI Attack Surfaces A key trend that we continue to see amongst our customers is digital transformation – transforming legacy and monolithic applications into decentralized, predominantly API-first applications that are distributed across multiple data centers, potentially across multiple cloud providers. That’s why organizations have a much bigger API attack surface today […]
A stylized topographical map with a warning sign at the peak representing attack detection and threat hunting
Bot Management

Attack Detection and Threat Hunting – Common Topics We’re Asked About

August 1, 2024

4

Read Blog
This article is the fifth in a series of five covering key API security topics and provides some answers to common questions we often get when talking to potential customers. The series will cover the following topics: API Discovery API Posture Management Attack Protection API Security Testing Attack Detection and Threat Hunting API security needs […]
Two stylized arrows chasing each other with a honeycomb design going through them representing API security testing
API Security

API Security Testing – Common Topics We’re Asked About

July 31, 2024

4

Read Blog
This article is the fourth in a series of five covering key API security topics and provides some answers to common questions we often get when talking to potential customers. The series will cover the following topics: API Discovery API Posture Management Attack Protection API Security Testing Attack Detection and Threat Hunting API security needs […]
A stylized shield with a checkmark on it laid onto a honeycomb background with concentric gradients from yellow to green to blue representing application and API attack protection
API Security

Application and API Attack Protection – Common Topics We’re Asked About

July 30, 2024

7

Read Blog
This article is the third in a series of five covering key API security topics and provides some answers to common questions we often get when talking to potential customers. The series will cover the following topics: API Discovery API Posture Management Attack Protection API Security Testing Attack Detection and Threat Hunting API security needs […]
A stylized image that looks like an audio mixer but the sliders have locks on them representing API posture management
API Security

API Posture Management – Common Topics We’re Asked About

July 29, 2024

4

Read Blog
This article is the second in a series of five covering key API security topics and provides some answers to common questions we often get when talking to potential customers. The series will cover the following topics: API Discovery API Posture Management Attack Protection API Security Testing Attack Detection and Threat Hunting API security needs […]
A stylized lock on a gradient honeycomb background representing API discovery
API Security

API Discovery – Common Topics We’re Asked About

July 26, 2024

3

Read Blog
This article is the first in a series of five covering key API security topics and provides some answers to common questions we often get when talking to potential customers. This series will cover the following topics: API Discovery API Posture Management Attack Protection API Security Testing Attack Detection and Threat Hunting API security needs […]
eBPF for API security
API Security

eBPF for API Security: The Devil’s in the Details

July 25, 2024

5

Read Blog
Application Programming Interfaces (APIs) facilitate seamless communication and data exchange between various software components, forming the connective tissue between modern enterprise applications. With the increasing dependence on applications and APIs, robust security measures are essential. The extended Berkeley Packet Filter (eBPF) is a promising technology for API security and traffic inspection. This blog explores how […]
CrowdStrike update brings BSOD (blue screen of death) to 1000s of Windows computers
Current Events

Blue Screened: Microsoft Windows Computers Crashed by Automated CrowdStrike Update

July 19, 2024

5

Read Blog
What Happened? Today, a significant global IT outage is broadly affecting diverse industries including aviation, banking, medical, technology, retail, and media due to a faulty content update published by security vendor CrowdStrike. Worldwide, thousands of computers running Microsoft Windows and CrowdStrike’s Falcon security software now show the Blue Screen of Death (BSOD) after receiving an […]
An architecture diagram depicting traffic flowing from a client to and from an F5 BIG-IP and mirrored to the Cequence platform. Traffic also flows from the F5 BIG-IP to applications and back.
API Security

Cequence Integration with F5 High Speed Logging (HSL) Enhances API Security Visibility

July 16, 2024

2

Read Blog
Cequence integrates with F5’s High Speed Logging (HSL) solution, providing another zero-latency passive deployment option. This integration enables Cequence to receive and process network traffic directly from the F5 appliance in order to discover and assess APIs and identify attacks. One of the Cequence Unified API Protection platform’s strengths from a customer perspective is its […]
API security solutions, Black Hat 2024, API security insights, Cequence Booth 2614, cybersecurity trends
About Cequence

Join Cequence Security at Black Hat 2024: Protect What Connects You

July 8, 2024

2

Read Blog
Protect What Connects with Cequence Application and API Security Solutions at Black Hat 2024 We are thrilled to announce that Cequence Security will be returning to Black Hat USA 2024 showcasing the latest in API security and bot management solutions. Held at the Mandalay Convention Center in Las Vegas on August 7-8, Black Hat is […]
Cequence - Best Workplaces
About Cequence

Raising Our Glasses to Cequence: We’ve Built One of The Best Workplaces in The Nation!

June 18, 2024

3

Read Blog
At Cequence Security, our journey has always been driven by a deep commitment to our team. We believe that a company’s culture isn’t just about words on a website or slogans on a wall—it’s about how our people feel, especially when the weekend draws to a close. It’s about trust, curiosity, drive, humor, and heart. […]
Stylized graphic of an infinity sign representing machine learning enhancements to the Cequence UAP Platform
Product News

New Machine Learning Enhancements to the Cequence UAP Platform

May 6, 2024

3

Read Blog
Cequence helps some of the world’s largest, most important organizations protect themselves from evolving threats, data breaches, and other business disruptions. As threats continue to evolve, so must software designed to prevent those unwanted outcomes. Cequence today announced several significant machine learning-based enhancements to its Unified API Protection platform including improved API discovery, API security […]
Verizon DBIR Insights – API Security
API Security

Verizon 2024 DBIR Insights

May 2, 2024

4

Read Blog
Cybercrime Christmas is here again in the form of the most excellent Verizon 2024 Data Breach Investigations Report (DBIR). If you’re into well-researched cybersecurity crime information, this annual report is for you. It’s a massive undertaking, and we’re all indebted to Verizon for making this happen each year. As in previous years, there’s a ton […]
API gateway security
API Security

Cequence Product Integrations – Broadcom Layer7 API Gateway

April 16, 2024

3

Read Blog
Today, we’ll spend some time talking about integrating Cequence solutions with the Broadcom Layer7 API Gateway. Broadcom API Gateway, previously known as Layer7 API Gateway, is an enterprise-grade solution designed to provide centralized management and security for API infrastructures. It acts as a proxy between clients and back-end services. Cequence Security offers customers numerous ways […]
HTML from one page being inserted into another, creating an iframe security risk representing an iFrame injection
API Security

What Are iframe Injection Attacks and How Do They Work?

April 11, 2024

4

Read Blog
Imagine your financial institution sends you an email that says you need to check something related to your account and the email contains a handy link to help you resolve the issue. You click on the link and the bank site loads, you login with your credentials and notice nothing out of place. Even though […]
OWASP top 10, OWASP API Security
OWASP

OWASP Top 10 Lists: Starting Point for Web & API Security

April 9, 2024

9

Read Blog
Made popular by television talk-show host David Letterman, an avid application security enthusiast and obsessive list maker, top 10 security lists have driven many organizations’ security programs, giving them a framework for a particular security initiative. In some cases, the lists have been used with tunnel vision, resulting in security gaps. While the OWASP Web […]
API security solutions at RSA conference 2024
About Cequence

Join Cequence Security at RSA Conference 2024: Protect What Connects You with Advanced API Security Solutions

April 8, 2024

2

Read Blog
Cequence Security is thrilled to announce our participation at this year’s RSA Conference, Booth 2033, where we’ll showcase our innovative bot management and API security solutions. The RSA Conference, a global summit for security innovators, returns to San Francisco’s Moscone Center from May 6-9. This event is a melting pot for those looking to exchange […]
API protection with Cequence and Vercara, API security
Product News

Comprehensive Application and API Protection with Cequence and Vercara

April 2, 2024

3

Read Blog
In January of this year, Cequence announced our partnership with Vercara, a leading provider of cloud-based security services. The partnership was motivated in no small part by the fact that Web Application Firewalls (WAFs) simply weren’t designed to handle the task of securing APIs. While WAFs and API gateways provide core application protection, they cannot […]
Stylized picture of a hill with wind flowing across it representing Cequence named to the Citizens JMP Cyber 66 List
About Cequence

Cequence Named to the Citizens JMP Cyber 66 List

March 28, 2024

3

Read Blog
Citizens JMP, a prestigious investment firm specializing in technology sectors, recently honored Cequence by recognizing us as one of the hottest privately held cybersecurity companies as part of its Cyber 66 list. This recognition highlights Cequence’s dedication to innovation and commitment to delivering solutions that effectively address the constantly evolving challenges of API security and […]
ChatGPT logo with a line going through it representing how hackers can use ChatGPT to launch automated attacks
Bot Management

How Hackers Can Use ChatGPT to Launch Automated Attacks

March 21, 2024

5

Read Blog
Key Takeaways: ChatGPT makes automated attacks much easier to carry out. LLMs like ChatGPT can generate code for attackers to deploy in seconds, with no hacking background required. IP blocking won’t cut it anymore. Today’s defense solutions must have multi-dimensional behavioral fingerprinting to identify attackers even as they retool to evade detection. Basic API Interrogation […]
Stylized image depicting lines transecting circles representing API threat detection
API Security

What is API Threat Detection?

March 19, 2024

4

Read Blog
API threat detection is one of the critical aspects of API security and is the process of identifying API threats intended to exploit API vulnerabilities. As API usage becomes more prevalent across organizations, they have also become a primary target of attackers, who employ widely varied and advanced techniques to exploit API vulnerabilities. Insufficient protection […]
Business logic abuse blog header image depicting information flowing through the internet and into a laptop.
Bot Management

What is Business Logic Abuse?

March 12, 2024

5

Read Blog
Business logic abuse is a common attack technique directed at web and mobile applications as well as their APIs. These attacks appear as valid interactions because the attacker is exploiting intended app or API functionality, which also enables them to bypass traditional security solutions without detection. These attacks can be automated and massively scaled through […]
Cequence International Women's Day - Inclusion in Cybersecurity
About Cequence

Inspiring Inclusion in Cybersecurity: Women Leading Change

March 8, 2024

3

Read Blog
Today is International Women’s Day, a day dedicated to celebrating the achievements of women worldwide and advocating for gender equality. As we prepare to mark this significant occasion, we are reminded of this year’s theme: “Inspire Inclusion.” This resonates deeply within the cybersecurity industry, prompting us to reflect on the progress made and the work […]
PSD2, the Future of Open Banking, and API Security
API Security

PSD2, the Future of Open Banking, and API Security

March 7, 2024

3

Read Blog
Open Banking Has Accelerated the Use of APIs – and the Need for API Security The landscape of open banking is rapidly evolving, fueled in no small part by the EU’s Revised Payment Services Directive (PSD2) aimed at enhancing authentication and regulating third-party access to financial data. Yet, despite its noble intentions, the journey towards […]
An anchor under water representing App Instrumentation
Bot Management

App Instrumentation: What It Is and How It Affects API Security

February 27, 2024

6

Read Blog
What is App Instrumentation? A simple Google search will reveal that app instrumentation is nothing more than embedding sensors within applications so their runtime behavior is observable. In the context of cybersecurity, this can help protect them from attacks. In actual fact, this “protection” is really “measuring” or “detecting”, i.e., sensing that an attack may […]
A chain link fence with a heart cut of it representing API security WAF and API Gateway
API Security

Why Do I Need API Security if I Have a WAF and API Gateway?

February 15, 2024

8

Read Blog
The web and mobile applications that your employees and customers use are glued together by application programming interfaces (APIs). The collaboration app on your phone “talks” to your collaboration system via APIs, allowing you to see who is online and message them. Your productivity, marketing automation, CRM, and project tracking apps are all API-based. As […]
Bots in hearts and a laptop with money funneling out of the laptop representing bot management and romance scams in dating apps
Bot Management

Broken Hearts and Empty Wallets: Romance Scams Plague Dating Apps

February 13, 2024

3

Read Blog
Every year around Valentine’s day, romance scams seem to rear their ugly heads. As more and more of our lives are online, it’s easier to meet people and get to know them without ever meeting in person. However, internet friendships and romances are also ripe for scammers and grifters looking to separate you from your […]
Cequence API Security for HPE GreenLake
About Cequence

Cequence and HPE GreenLake: API Security for Cloud Native Applications

February 6, 2024

2

Read Blog
In the rapidly evolving landscape of cloud native infrastructure, APIs stand as crucial conduits, powering everything from online shopping to mobile applications. However, this increased connectivity introduces significant security risks, with APIs often operating without sufficient oversight. Many of the recent data breaches making headlines were due to APIs that were improperly secured. As digital […]
A paper on top of a honeycomb pattern representing the Who, What, and Why of API Specifications
API Security

The Who, What, and Why of API Specifications

February 1, 2024

7

Read Blog
Here at Cequence we have covered the ups and downs of API specs throughout the years. Discussions on what they are, who is (and regrettably isn’t) using them, and why they are important have been the subject of several blog posts on our site and around the web. We’ve discussed the OpenAPI Specification (OAS) and […]
Unified API Protection Platform Recognized by KuppingerCole
Industry Reports

KuppingerCole Recognizes Cequence Unified API Protection Platform

January 30, 2024

3

Read Blog
API security continues to elevate in terms of awareness and importance in both government and commercial sectors. Organizations need to ensure that their APIs are secure, protected from attacks, abuse, fraud, and data losses. With a multitude of vendors offering products under the umbrella of API security it can be confusing for organizations trying to […]
A city scape in the clouds made from servers representing API protection and security
API Security

Embracing Diversity: Unified API Protection in Heterogeneous Environments

January 25, 2024

4

Read Blog
As business infrastructure grows, it necessarily becomes more diverse and heterogeneous. Relatively simple on-premises environments have exploded into an ever-growing range of applications and architectures including cloud, hybrid, multi-cloud, monolithic, microservices, and serverless. The need to innovate and provide exceptional customer experiences in fields such as ecommerce, Big Data, IoT, AI, and cloud computing is […]
API security - Product Blog - 2024
About Cequence

Cequence End of Year Product Recap – Strengthening Your API Security

January 23, 2024

3

Read Blog
As we bid farewell to an eventful year, we are excited to recap the strides we’ve made in enhancing our products to further strengthen your API security. In 2023, we’ve focused on the key themes that directly impact you: Usability Improvements and Eliminating Friction: Your experience with our products matters, and we’ve dedicated efforts to […]
Cequence best places to work
About Cequence

Cequence Stands Out: Recognized as a Top Workplace by Built In

January 17, 2024

4

Read Blog
Last week’s announcement brought the exciting news that Cequence was recognized in the prestigious 2024 Best Places to Work Awards by Built In. This recognition underscores our unwavering commitment to building a workplace culture that esteems innovation, collaboration, and the well-being of our remarkable team. Acknowledging Cequence’s exceptional workplace environment, employee satisfaction, and dedication to […]
A gavel on a honeycomb pattern representing regulations and standards affecting API Security
OWASP

Regulations and Standards Shine a Much-Needed Light on the Need for API Security

December 20, 2023

6

Read Blog
APIs have become integral to modern software architecture, and the digital economy has exponentially increased API adoption. However, with the rise of APIs, there has been a corresponding rise in API security risks. Capturing today’s headlines are API-origin data breaches that have compromised tens of millions of sensitive customer records. This dramatic increase in API-based […]
Binoculars looking at 2024 representing Cequence - 2024 Predictions: Compliance, API Security Threat Tactics, and AI
API Security

2024 Predictions: The Changing Regulatory Environment, API Security Threat Tactics, and AI

December 18, 2023

4

Read Blog
Looking forward to 2024, we can confidently make some predictions based on our ongoing analysis of API attacks and the behavioral changes we are seeing as attackers refine their strategies. One thing we can be sure of – as organizations continue to increase their reliance on APIs to share data between applications, cybercriminals will continue […]
The Cequence 2023 Holiday Season API Security Threat Report unveils some surprising trends and attacks against retail businesses.
CQ Prime Threat Research

Cequence 2023 Holiday Season API Security Threat Report – Retail Fraud Up Nearly 700%

December 14, 2023

7

Read Blog
Retail cybercriminals have graduated from relatively quick, unsophisticated smash and grab-style attacks to playing the long game, spreading attacks out over the course of the year in preparation for a holiday season bonanza. This shift in tactics has come to light in the latest threat intelligence research from the Cequence CQ Prime Threat Research team […]
A line of open doors letting light in, representing how to block API attacks the right way.
API Security

Everybody Blocks API Attacks, Right?

December 11, 2023

5

Read Blog
Many API security vendors claim to have products that detect and block API attacks. Like many security product categories, a bit of investigation is warranted when reviewing such claims. For example, many of these vendors offer some level of automated bot attack detection but cannot natively block these attacks. They instead rely on other infrastructure […]
Cequence CFO perspective on the financial implications of data breaches
API Security

Safeguarding Financial Health: Why CFOs Should Prioritize API Security

November 1, 2023

5

Read Blog
In today’s rapidly evolving digital landscape, businesses are increasingly relying on Application Programming Interfaces (APIs) to drive innovation, streamline operations, and enhance customer experiences. However, as organizations harness the power of APIs, a new and critical concern arises: API security. While it might be tempting for CFOs to leave the technicalities to the IT or […]
Cequence FFIEC API security Dodd-Frank Section 1033
API Security

Navigating the New CFPB Rule on Open Banking: The Details

October 20, 2023

3

Read Blog
Our sources in Washington were right. The Consumer Financial Protection Bureau (CFPB) announced with the rule and set forth an ambitious goal that’s bound to redefine the contours of the financial world. Let’s unpack this significant shift to understand its nuances and implications: Key Highlights of the CFPB Proposal: Current state: The CFPB estimates that […]
Cequence - CFPB to Announce Major Open Banking Proposed Rule
API Security

CFPB to Announce Major Open Banking Proposed Rule

October 18, 2023

2

Read Blog
Consumer Financial Protection Bureau (CFPB) to Release Major New Proposed Rule on Thursday October 19 Cequence’s contacts in Washington D.C. indicate that the Consumer Financial Protection Bureau (CFPB) will publish their major rule on Dodd-Frank Section 1033 (Open Banking / Open Finance) Thursday, October 19, 2023. The rule is expected to be a key milestone […]
Cequence Security Awarded Best Enterprise Cybersecurity Solution of the Year
API Security

Cequence Security Awarded Best Enterprise Cybersecurity Solution of the Year

October 5, 2023

2

Read Blog
Cequence Security is pleased to announce that the Unified API Protection Platform has been named the Enterprise CyberSecurity Solution of the Year in the 2023 CyberSecurity Breakthrough Awards for the second year. The awards program is conducted by CyberSecurity Breakthrough, a leading independent market intelligence organization that recognizes the top companies, technologies, and products in […]
The Duolingo bird with tears in it's eyes representing the API breach
API Security

Essential Lessons from the Duolingo API Breach

September 19, 2023

6

Read Blog
Duolingo is one of the largest and most popular language learning apps in the world. In August of 2023, it was reported that data on 2.6 million Duolingo users – including names, email addresses, and more – had been leaked onto a hacking forum. Duolingo’s API for user account access only required an email address, […]
Cequence API Security Breaches
API Security

What We Have Learned from Recent API Security Breaches

September 12, 2023

4

Read Blog
API Security Breaches – Lessons learned In the digital age, APIs (Application Programming Interfaces) have become the backbone of modern application architecture, enabling seamless integration and communication between various software applications. The increasing reliance on APIs has also opened up new avenues for cyber threats: recent API security breaches have underscored the importance of robust […]
Cequence OWASP API Top 10
API Security

Understanding the Evolution of OWASP API Security Top 10 from 2019 to 2023

September 5, 2023

5

Read Blog
The Open Web Application Security Project (OWASP) is a non-profit organization dedicated to improving software security. One of their most well-known projects is the OWASP API Security Project, which aims to provide a foundational set of security controls for APIs. In this post, we’ll explore the changes introduced in the 2023 version compared to the […]
Cequence FFIEC API security Dodd-Frank Section 1033
API Security

FFIEC API Security Guidance for Financial Services

September 1, 2023

5

Read Blog
In an era where technology is the cornerstone of the financial industry, safeguarding sensitive information and maintaining the integrity of data has become paramount. Financial institutions are constantly faced with the challenge of ensuring the security of their systems, especially when it comes to Application Programming Interfaces (APIs) and API security. The Federal Financial Institutions […]
API Security - The Cyber Top 20 Award - Cequence Security
API Security

Cequence named winner in the Enterprise Security Tech 2023 Cyber Top 20 Awards List

August 9, 2023

2

Read Blog
Cequence is pleased to announce that we have been named to the Enterprise Security Tech 2023 Cyber Top 20 Awards List for our Unified API Protection (UAP) platform! The Cyber Top 20 honors organizations shaping the future of cybersecurity and those that have redefined the approach to protection and defense. The Cequence UAP platform is […]
IDOR vulnerability
CQ Prime Threat Research

Understanding the Joint Cybersecurity Advisory on IDOR Vulnerabilities by ACSC, CISA, and NSA

July 31, 2023

5

Read Blog
The Australian Signals Directorate’s Australian Cyber Security Centre (ACSC), U.S. Cybersecurity and Infrastructure Security Agency (CISA), and U.S. National Security Agency (NSA) released a joint Cybersecurity Advisory on July 27, 2023, to warn vendors, designers, and developers of web applications and organizations using web applications about insecure direct object reference (IDOR) vulnerabilities also known as […]
Best-in-class API Security - Datos Analyst Report
API Security

Cequence Ranked as Best-in-Class API Security Among All Vendors

July 27, 2023

7

Read Blog
Introduction After winning numerous industry accolades and awards, we are very pleased to announce the latest feather in our cap, where Cequence was named a Best-in-Class API Security solution among all vendors by Datos Insights (formerly known as Aite-Novarica). The Datos Insights Vendor Evaluation is a comprehensive, proprietary process that is designed to provide a […]
Unified API protection award, Best API Security award
API Security

Cequence Security’s Unified API Protection Solution Wins Three 2023 Globee<sup>®</sup> Awards

July 19, 2023

2

Read Blog
We are proud to share that our Unified API Protection platform has been honored as a gold winner in the 18th Annual 2023 Globee® Awards for Information Technology in Application Programming Interfaces (API) Management, Full Life Cycle API Management, and IT Solutions for Retail categories. These esteemed global awards celebrate outstanding achievements in information technology […]
Bot Management

Prep the Halls: Readying Your Retail Environment for the Holiday Rush

July 1, 2023

5

Read Blog
Long before the clock ticks past midnight into the morning hours of Black Friday, excited shoppers are eagerly preparing to hit the pavement and the websites of their favorite retailers. Using ecommerce applications for retailers across the globe, everyone is scoping out potential buys in the hopes of finding those deals and the hot products […]
API Security Testing with Generative AI
API Security

Cequence Unveils Groundbreaking API Protection with Generative AI and No-code Security Automation

June 26, 2023

8

Read Blog
Enriches Unified API Protection with Advanced Fraud Prevention & Enhanced Testing Capabilities APIs are the currency of business exchange driving innovation and commerce. In fact, IDC estimates that up to 50% of enterprises’ revenues are enabled over APIs, translating for example to over $161 BILLION in Telecom revenues year before last. This has resulted in […]
MOVEit vulnerability
API Security

API 0Day Response – a MOVEit story

June 20, 2023

4

Read Blog
June 9th Progress Software released a statement “Multiple SQL injection vulnerabilities have been identified in the MOVEit Transfer web application that could allow an unauthenticated attacker to gain unauthorized access to the MOVEit Transfer database.” Well, that doesn’t seem very good at all, in this case “multiple” meant 3 on June 15th with a 0Day […]
DBIR API Security - Unveiling Critical Insights on Data Breaches
API Security

Unveiling Critical Insights on Data Breaches: Exploring the Latest Verizon DBIR and the Role of API Security

June 6, 2023

7

Read Blog
The digital landscape is fraught with ever-evolving threats, making it crucial for organizations to stay informed about the latest trends in data breaches and cyber-attacks. The Verizon Data Breach Investigations Report (DBIR) serves as a valuable resource, providing deep insights into the current threat landscape. One crucial thing missing in the earlier versions of the […]
Unified API Protection Telcom
Customer Case Studies

Unified API Protection for Telcos and Mobile Carriers – Time to Value

May 26, 2023

3

Read Blog
Largest Mobile Carrier Identified 4,600 APIs in Days, not Weeks, or Months The security team at the nation’s largest mobile carrier had a problem trying to obtain a consistent and complete inventory of the company’s sprawling API footprint. Business critical API-based applications were driving the mobile carrier’s day-to-day business of managing their mobile network, but […]
API Threat Research Report
API Security

API Threat Research Validates Robust API Security Program with Automated API Attack Mitigation Capabilities

May 16, 2023

4

Read Blog
API threat research by the Cequence CQ Prime Threat Research team during the second half of 2022 confirms that API security and API attack mitigation are two sides of the same coin, and both are essential to ensure the security of APIs. Attackers continue to use tried and true techniques to find and exploit shadow […]
API Security for Financial Services
API Security

API Security for Financial Services

May 2, 2023

8

Read Blog
When it comes to the global financial services industry which includes banks, credit unions, exchange houses, finance companies, payment card issuers, and insurance companies, API security is a top priority. It only takes one data breach or persistent fraud because of an API exploit or abuse to damage an organization’s reputation and get the attention […]
RSA Conference - booth traffic, RSAC
API Security

API Security the Number One Topic at 2023 RSA Conference

April 26, 2023

3

Read Blog
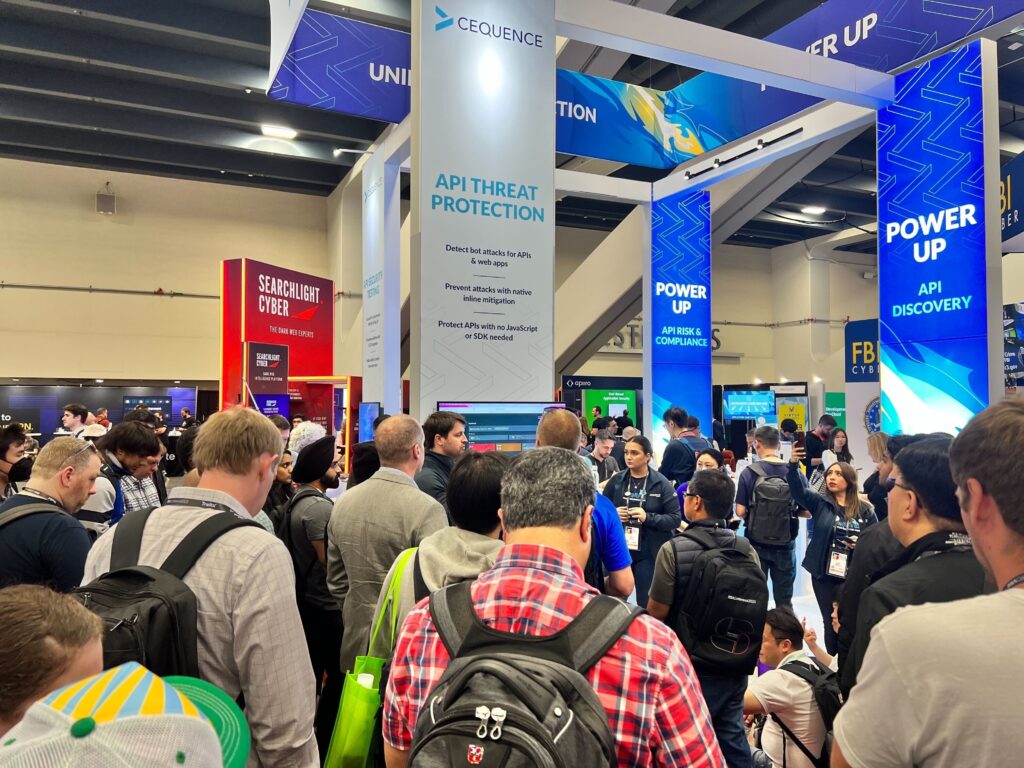
Cequence, the largest API security company in the world is powering up at booth 0455 at the RSA Conference talking to cybersecurity professionals and enthusiasts from around the world about API security. With API security the number one topic, along with artificial intelligence, and the potential benefits in the field of cybersecurity top of mind […]
API Security - Connected Car Safety & Security
API Security

Automotive API Security for Connected Vehicles

April 12, 2023

7

Read Blog
APIs used in connected vehicle systems offer points of entry for hackers and other malicious actors to exploit cars, trucks, telematics devices, and fleet management operators. In this blog you’ll learn what’s needed for an effective API security program to ensure vehicle safety and security for the entire API protection lifecycle. The average vehicle has […]
API Security Plan
API Security

How to Approach API Security in 2023: Your 30-60-90 Day Security Plan

March 28, 2023

6

Read Blog
API security is a top 2023 security initiative for many organizations, given the continued increase in API usage and the API breach activity observed in 2022. Since more and more organizations are starting API security programs, I thought it might be prudent to provide a 30-60-90 day framework that we are all pretty familiar with. […]
API Security Automation
API Security

How Security Automation Strengthens API Security

March 2, 2023

6

Read Blog
Learn how customers are leveraging security automation to accelerate bot attack response time and improve their API security posture. In effect, customers can fight fire with fire by using automation to block (automated) bot attacks like account takeover, shopping bots and loan fraud. Every IT security professional I know, or meet is overworked. This is […]
API Protection in Finance
Customer Case Studies

Financial Services Firm Reduces Threat Protection Response Time From 3 Hours to 30 seconds

February 24, 2023

4

Read Blog
A large global investment firm operates globally with over $7 trillion dollars in assets. It offers a wide variety of financial products to over 30 million retail investors that rely on this firm to manage their investment and retirement accounts. Their clients expect easy, secure, and uninterrupted access. Key API Application That Powered Customer Access […]
A Winning Trifecta: API Gateways, API Security and API Protection
API Security

Improved API Security Through Unified API Protection and API Gateway Integration

February 13, 2023

4

Read Blog
The Cequence Unified API Protection solution integrates with a wide range of API gateways, complementing their API security features with API discovery, risk analysis and threat protection. API gateways are a key element in the quest for API security and API protection, acting as the focal point for API calls between the client and the […]
API Security Testing and API Spartan
Product News

Cequence Announces API Security Testing, Extending Their Lead in Unified API Protection

February 13, 2023

7

Read Blog
We are excited to announce Unified API Protection v2.0, the latest release of our market leading API security platform. Unified API Protection v2.0 adds dynamic API Security Testing to the platform to help security and development teams find and remediate API vulnerabilities before they are released to production. In addition to the new API Security […]
Telecommunications API Security
Bot Management

Rapid Response Blocks Large API-based Phishing Campaign – Telecommunications API Security

February 10, 2023

3

Read Blog
A large telecommunications API security customer with over 100 million mobile subscribers detected and blocked a sophisticated API-based phishing attack in a matter of hours, highlighting a rapid API security time-to-value provided by the Cequence Unified API Protection (UAP) solution. With many applications that support their mobile business, their IT security team is constantly on […]
Unified API Protection
API Security

Unified API Protection: Making Today’s API Landscape Secure

February 5, 2023

5

Read Blog
A massive segment of organizations’ digital footprint today is built around internal and external APIs. As more IT leaders realize and acknowledge the size of APIs’ influence, it’s become clear that new methods are needed to secure those APIs. While many companies today use the term “API security” to describe their offerings, these solutions often […]
Account Takeover Financial, Financial Services ATO Prevention
Bot Management

Financial Services Customer Stops Millions of API-based Account Takeover Attacks (ATO)

February 2, 2023

4

Read Blog
Using the Cequence Unified API Protection (UAP) solution, a Fortune 100 financial services customer detected and blocked a large-scale account takeover (ATO) attack that targeted their mobile APIs. Attackers analyzed perfectly coded APIs found in the mobile application to understand how they work. Then, using commercially available attack tools combined with the billions of readily […]
API Security Meets Government Regulators
API Security

API Security Meets Government Regulators

February 1, 2023

4

Read Blog
The Australian Cyber Security Centre (ACSC) leads the Australian Government’s efforts to improve cyber security and recent data breaches and the potential theft of private data, have put a spotlight on API security. API Abuses and Related Data Breaches The ACSC provides a valuable service as businesses continue to move more of their operations to […]
API Security 101
API Security

API Security 101

January 31, 2023

6

Read Blog
What Is API Security API security means protecting the APIs and their associated digital assets. With so much of our digital world supported by APIs, the need for API security is staggering. The speed of API adoption had far outpaced most organizations efforts to apply oversight or implement appropriate API security measures. The shopping, financial […]
API Security - Patching Gaps, LoNg4j, Log4j vulnerability
API Security

Best Practices for Addressing Log4j and LoNg4j Patching Gaps

January 27, 2023

5

Read Blog
Long after the press news and panic surrounding the discovery of Log4j, the Log4 Shell exploit and the supply-chain variant dubbed LoNg4j, IT and security teams are still struggling to adopt Log4j best practices for ensuring their servers are patched and protected. To help our customers address this critical need and improve API security, we […]
API Security - API bot abuse
CQ Prime Threat Research

API Security: API10+ Defined as Bots Abusing Well-Formed APIs

January 26, 2023

6

Read Blog
API business logic abuse, informally defined as as OWASP API10+, an extension to the OWASP API Top 10, is the practice of attacking perfectly coded APIs to achieve a malicious end-goal. Coding errors like weak authentication, excessive data exposure or the inadvertent publication of internal APIs are all known to be root causes of recent […]
API Security - Sensitive Data Exposure
CQ Prime Threat Research

How BOLA Vulnerabilities Can Expose Sensitive Data: API Security Report

January 24, 2023

8

Read Blog
New threat research for API security, this blog walks through the discovery of a Broken Object Level Authorization or BOLA vulnerability (OWASP API1) by the CQ Prime Threat Research Team that could be used to exfiltrate sensitive (customer) data. It’s well known that attackers can use stolen PII to apply for credit card accounts, government […]
API Security

Survey Highlights API Business Value and API Security Balancing Act

January 24, 2023

6

Read Blog
Survey Highlights API Business Value and API Security Balancing Act Much like the plumbing in our homes that works behind the scenes to make our lives easier, APIs are quietly helping organizations large and small generate significant business value APIs silently help us purchase nearly anything we need from our living room and have it […]
API Security - Chess
CQ Prime Threat Research

API Security Bypassed Using Multiple OWASP API Threats

January 20, 2023

5

Read Blog
Research by the CQ Prime Threat Research Team documents how attackers leveraged multiple OWASP API Top 10 threats including Broken User Authentication (API2), Excessive Data Exposure (API3) and Improper Assets Management (API9) to achieve their end goal. The practice of mixing and matching the OWASP API Top 10 categorized threats to bypass API security is […]
CQ 2023 Predictions
API Security

2023 Predictions: Staying One Step Ahead in API Protection

January 19, 2023

7

Read Blog
API Abuses and Related Data Breaches Gartner has said that API attacks would be the most common attack vector in 2022, resulting in data breaches for enterprise web applications. Gartner also predicts that by 2024, API abuses and related data breaches will double. For 2023, we don’t see any reason to doubt that APIs will […]
Operational Tech
API Security

API Security in Your Operational Technology (OT)

January 19, 2023

6

Read Blog
Operational technology encompasses supervisory control and data acquisition (SCADA), industrial control systems (ICS), and distributed control systems (DCS). OT can be involved in critical processes that, if breached, could have catastrophic consequences, including loss of life. Water treatment plants, power distribution, traffic management, and other critical infrastructure rely on operational technology solutions to properly function. […]
API Security - Third Party API's
CQ Prime Threat Research

API Security Lacking for Ecosystem and Third-Party APIs?

January 18, 2023

8

Read Blog
Research by the CQ Prime Threat Research Team documents how attackers bypass API security to target third-party and partner eco-system APIs to achieve their end-goals. In the latest research report, attackers hit APIs supporting a financial services partner eco-system, ApplePay and a third-party inventory lookup. Third-party and Eco-system APIs are not New Long before APIs […]
Customer Case Studies

Telecom API Security: Shadow API Protected in Less Than 30 Minutes

January 17, 2023

3

Read Blog
Today’s blog highlights how an existing telecom API security customer was able to discover and protect a shadow API that was under attack in less than 30 minutes. Highlighting a common theme of rapid-time-to-value, this customer benefited from the Cequence approach to bot protection that eliminates the cumbersome SDK or JavaScript integration requirement. Agentless bot […]
Real-Time API Threat Prevention - Proactive
API Security

Why is Real-Time API Threat Prevention a Must-Have?

January 16, 2023

9

Read Blog
The ability to prevent an API attack in real-time, without relying on integration with a WAF, or other tool is a must-have API security requirement. Native, or real-time API threat prevention ensures you respond to the attack as quickly and efficiently as possible. The difference between relying on a third-party and real-time prevention is like […]
UAP & CDN API Protection Integration
API Security

Complete API Security with Cequence UAP and CDN Integrations

January 16, 2023

4

Read Blog
Cequence Unified API Protection integrates with the leading content delivery network (CDN) solutions such as Akamai, Amazon, CloudFlare, and Fastly, complementing their basic API security features to ensure all APIs are discovered, analyzed and protected, regardless of location. CDNS were originally designed to help organizations optimize their public facing web and API-based application content delivery. […]
API Threat Research - API Protection Report
CQ Prime Threat Research

New API Threat Research Shows Shadow APIs as the Top Threat Vector

January 15, 2023

5

Read Blog
API threat research by the Cequence CQ Prime Threat Research team confirms shadow APIs are the top threat challenging the industry with 31%, or 5 billion malicious transactions observed in the first half of 2022 targeted unknown, unmanaged and unprotected APIs, commonly referred to as shadow APIs. Top API Threat Research Findings The data, drawn […]
Retail API Security - Pizza Chain
Customer Case Studies

Credential Stuffing Attack Prevention Saves $1.6M

January 13, 2023

3

Read Blog
In another example of pandemic influenced actions, the largest Canadian pizza chain was targeted by a credential stuffing attack that was successfully mitigated resulting in a $1.6M savings. Most people would not imagine pizza as a cybercrime target but remarkably Canada’s largest retail pizza chain had been experiencing just that, a set of ongoing cyberattacks […]
API Security

Unified API Protection: A Solution Whose Time Has Come

January 9, 2023

6

Read Blog
Unified API protection is defined as the ability to secure your APIs across every phase of the application protection lifecycle. To ensure business success, security teams must prevent misuse, abuse, fraud, data loss and non-compliance across their legacy web and mobile application connections, but now even more importantly over the APIs that the business depends […]
API Security Checklist
API Security

Using an API Security Checklist: What Should You Look For?

January 6, 2023

8

Read Blog
When asked how to define API security, most security professionals would say it means protecting your APIs. Asking a second, more specific question of what are the API security solution requirements needed to address the explosive use of APIs and the corresponding increase in malicious activity will result in a more detailed answer. This is […]
API Specification Framework Best Practices
API Security

API Security Best Practices: Using OpenAPI to Improve API Security

January 4, 2023

6

Read Blog
The adoption of API specification frameworks like OpenAPI (OAS) encourages documentation best practices resulting in higher quality, more consistent API coding and improved API security. Historically, APIs were designed for machine-to-machine communications, and were rarely documented resulting in lower quality APIs and making it difficult to achieve the goals of catching security flaws earlier. Using […]

Get an Attacker’s View
into Your Organization


Schedule A Demo