
USE CASE
Secure Agentic AI in the Enterprise
Unlocking the Promise of Agentic AI Productivity with Security, Visibility, Governance, and Control
Organizations are racing to harness agentic AI for productivity gains, competitive advantage, and growth. Company boards impose aggressive deadlines while CISOs demand security guarantees and CIOs struggle with fragmented prototypes that can’t scale. The gap between ambition and reality widens daily.
Leading Uses for Agentic AI
Internal Productivity
Organizations want to empower employees to higher productivity while maintaining visibility and control over agent-system interactions.
Product / Engineering
- Track project status, active incidents, and open issues.
- Accelerate incident response and debugging.
- Improve team coordination with automated workflows.
Sales / Marketing
- Automate lead qualification by connecting data to pipeline.
- Improve customer qualification and pipeline insights.
- Generate data-driven forecasts and reports.
Security Operations
- Accelerate threat detection and incident response.
- Improve SOC team efficiency by AI-enhanced prioritization.
- Generate reports and remediation efforts for urgent issues.
Customer-Facing Applications
Delivering positive and seamless customer experiences while protecting against data leakage, business logic abuse, and unauthorized access is key.
Customer Success
- Track customer status, open issues, feature requests.
- Generate quarterly customer review reports.
- Accelerate incident and inquiry responses
E-Commerce
- Autonomous product advisor and shopping companion.
- Natural language processing enables richer customer experience.
- Democratized access to limited edition goods.
The Enabling Protocol
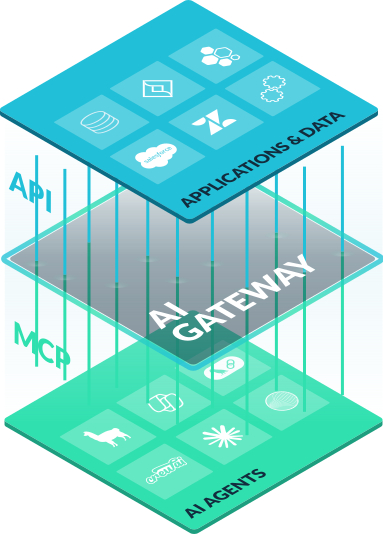
Model Context Protocol (MCP) is the de-facto standard translation layer connecting AI agents to enterprise applications and data. The standard enables rapid prototyping, but building for production demands more. As multiple departments create their own implementations, organizations face interoperability issues, data security gaps, and lack of governance when attempting to move to production and scale.
Agentic AI Security Concerns
Agentic AI introduces the possibility of attacks both common and novel, for which traditional security tools weren’t designed to handle.

Rogue MCP Servers
Developers download and use untrusted MCP servers from the internet, creating backdoors into enterprise systems. “Typosquatting” attacks impersonate legitimate integrations. Malicious MCP servers can exfiltrate data or cause other damage while appearing to function normally. Without a trusted registry of MCP servers and monitoring of their actions, organizations cannot distinguish safe from dangerous.

Business Logic Abuse
AI agents adapt behaviors in real time, mimicking legitimate users to bypass defenses that lack business context. They identify and exploit logic flaws faster than human attackers, prioritizing profitable abuse paths. Rate limiting and signature-based detection fail against this sophisticated threat.

Data Exfiltration
Broad permission scopes grant unnecessary access. Agents pull sensitive data across service boundaries. Organizations lose visibility into what data agents touch and where it goes. The results are lost intellectual property and customer data, compliance violations, and more.

Insufficient Guardrails
AI agents are non-deterministic, potentially generating different outcomes from the same input. An agent operating from a valid request might attempt to access data or execute programs it shouldn’t in pursuit of fulfilling its goal. Organizations must have proper guardrails in place or risk agents operating outside trust boundaries.
Enterprise Requirements for Enabling Agentic AI
Enterprises must demand certain capabilities from partners that provide agentic AI enablement solutions in order to safely and securely put their projects into production.

Established Vendor Reliability
Partners who provide enterprise SLAs, 24/7/365 support, and long-term commitment

Built-in Authentication and Authorization
OAuth 2.1 integration, support for Zero Trust principles including continuous verification of identity and permissions

Security and Monitoring
Real-time visibility into user-agent-API traffic, detection of malicious use and business logic abuse, comprehensive audit logging

Trusted MCP Registry
Vetted, secure server implementations that eliminate rogue server risks

Governance and Cost Control
Consistent standards for MCP versions, server creation and usage policies, protection of sensitive data
Cequence AI Gateway: Secure Agentic Enablement
Cequence bridges the gap between prototype and production, delivering secure agentic AI enablement in minutes instead of months.
No-Code Enablement
The Cequence AI Gateway makes any internal, external, or SaaS application agent-ready without writing code. Upload OpenAPI/Swagger specs or select existing APIs to transform endpoints into MCP-compatible tools. Avoid upskilling developers or creating technical debt.
Enterprise-Grade Authentication and Authorization
Integrate OAuth 2.1-compliant identity providers in minutes. Enforce identity-based access to systems and data and prevent unauthorized AI agent access. Support Zero Trust architectures with continuous authentication and authorization.
Built-In Trusted MCP Registry
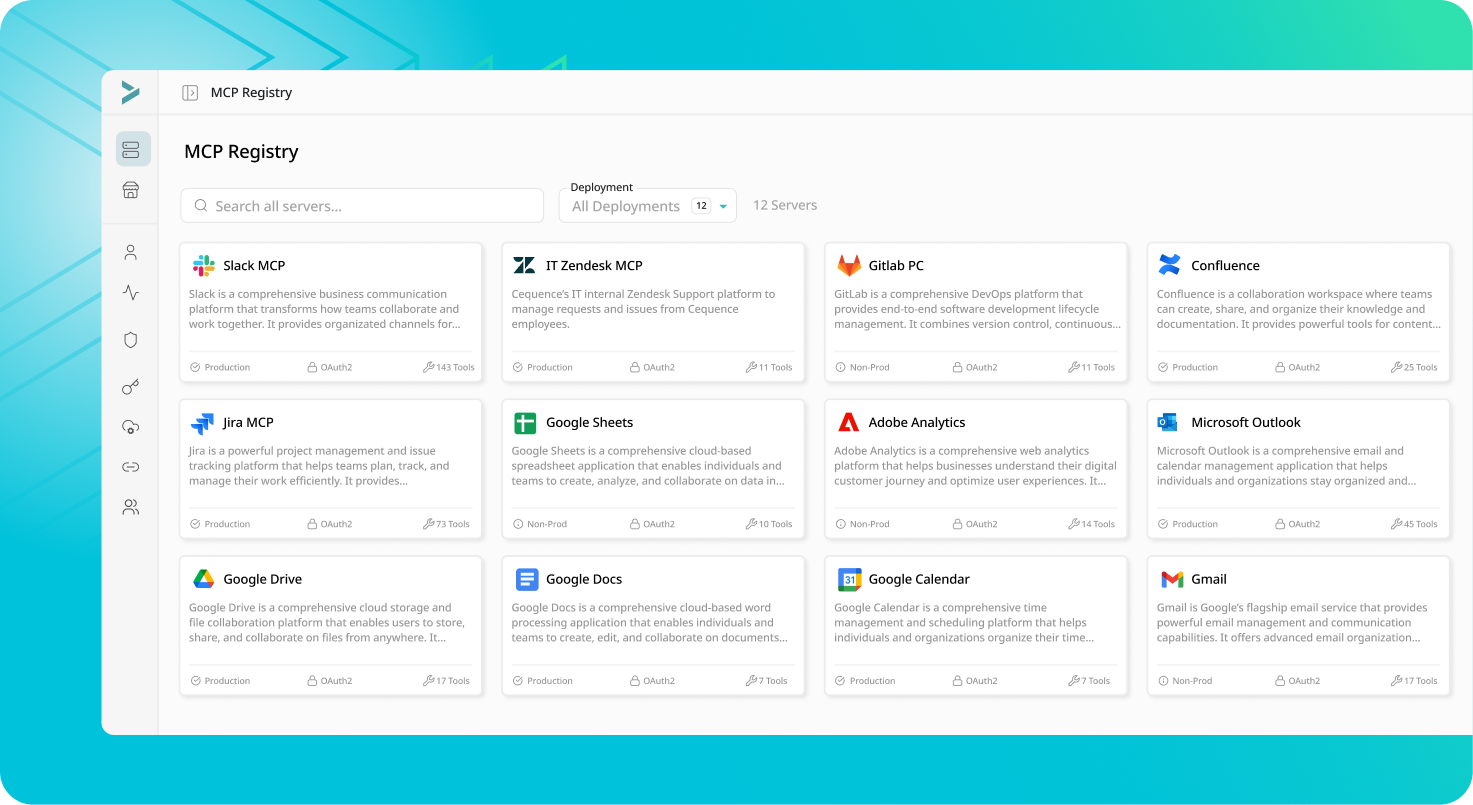
Eliminate rogue server risks with pre-vetted MCP servers. Teams access only approved servers that meet security and governance standards. Official APIs become trusted MCP endpoints instantly.
Comprehensive Visibility and Monitoring
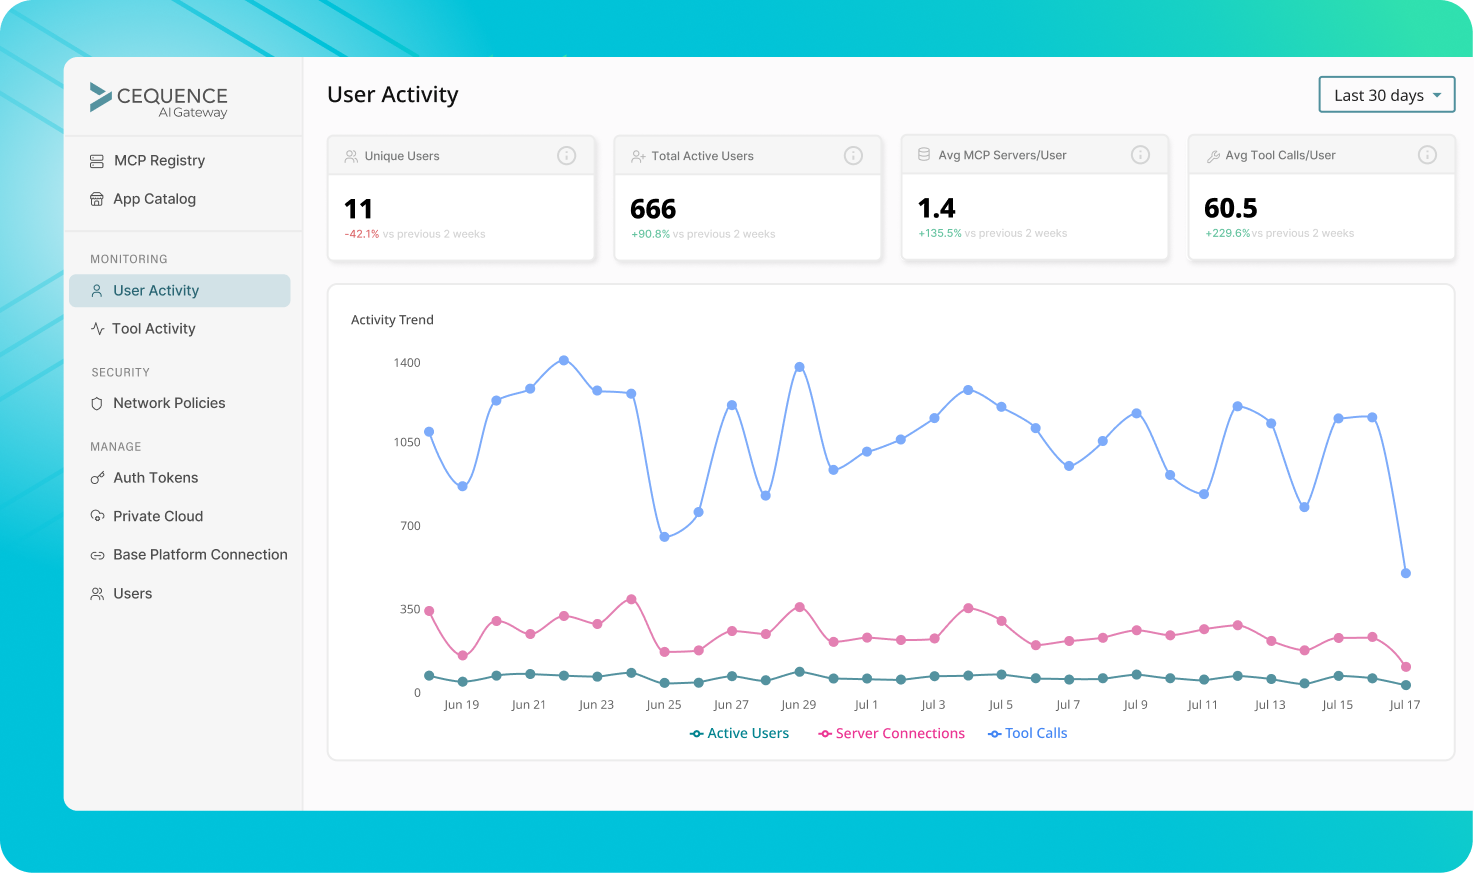
Track every agent-API interaction through a real-time dashboard. Log which applications agents access, what API calls they make, and what data they touch. Identify suspicious patterns before they become breaches.
Abstract Protocol Changes
Protect investments as standards evolve. AI Gateway abstracts updates to MCP and other emerging protocols, ensuring applications remain compatible without reengineering.
Flexible Deployment
Deploy in Cequence Cloud for instant value or manage private cloud deployments for maximum control. Have confidence in scalable deployments backed by SLA guarantees.
Part of the Cequence Platform
Leverage Cequence’s expertise in API security and bot management to identify agent-fueled attacks, exploits, and business logic abuse. AI agents are API consumers, and Cequence built its reputation securing applications, APIs, and data at scale.
Learn more about the Cequence Platform
Additional Resources
Cequence Security application and API protection experts will show you how we can help you improve your security posture with a personalized demo. Nothing to deploy. All we need is your email.
Personalized Demo