
USE CASE
API Discovery and Inventory
API Discovery: The Foundation of Application and API Security
APIs are the connective tissue between modern applications. They enable innovation, accelerate digital transformation, and connect services across cloud, mobile, and on-premises environments. But that same ubiquity creates risk. Most organizations today don’t actually know how many APIs they have or where all of them live. API discovery and inventory form the foundation of a strong API security program, ensuring visibility, control, and governance across every API that touches your environment, whether internal, external, or third-party.
What Makes Up Complete API Discovery and Inventory?
A complete API inventory goes far beyond a simple list of endpoints. Ideally, it’s a living, detailed record of every API asset in your ecosystem, providing a strong foundation for effective monitoring, risk assessment, and compliance management. A robust inventory should include:

Attack surface discovery
provides an attacker’s view of the API hosts and endpoints that are available

Runtime discovery
identifies APIs via traffic, enabling the discovery of known APIs as well as shadow and zombie APIs

API definitions
API specifications that provide an understanding of how an API should function

API data flows
documents, sometimes visually, how data flows between multiple network components including APIs
Hosts and their API endpoints
a comprehensive inventory should include API hosts as well as their endpoints

Shadow APIs
undocumented API endpoints whose Host/BasePath match an existing API definition

Data sensitivity
automatically detecting whether the API transacts sensitive data or not

API specification drift
API endpoints with detected characteristics that deviate from the specification

API scope
identifying each API as internal, external, or third-party
How API Sprawl Outpaces Manual API Discovery
APIs evolve constantly. New services are deployed, old ones are retired, and third-party connections change. Even a comprehensive inventory can drift out of date quickly if it’s not maintained automatically. When inventories lag, “API sprawl” occurs and security teams lose situational awareness. An out-of-date API inventory can cause the proliferation of shadow APIs, zombie APIs, and untracked third-party drift. Gaps appear between what’s documented and what’s actually live, creating the perfect environment for attackers to thrive.
The Security Risks of Outdated API Inventories
An incomplete or outdated API inventory invites API risk. You can’t protect what you can’t see, and unseen APIs are often the easiest to exploit. Without automated API discovery, organizations face:

Increased Attack Surface
Unknown and unmanaged APIs provide new entry points for attackers


Compliance Violations
Unmanaged APIs handling regulated data can lead to PCI DSS, HIPAA, or other violations

Bot Exploitation
Automated attacks target APIs for scraping, credential stuffing, or business logic abuse

Delayed Incident Response
Should a breach occur, outdated API inventories can slow investigation and remediation
Cequence Powers Automated API Discovery and Inventory
Cequence Security eliminates the visibility gap with comprehensive API discovery and inventory management. The Cequence Platform automatically discovers all APIs — internal, external, and third-party — across your environment.
Attack Surface Discovery
API discovery starts outside the perimeter. Provides an attacker’s view into an organization’s public-facing resources to identify external API hosts, unauthorized hosting providers, and API-specific security issues.
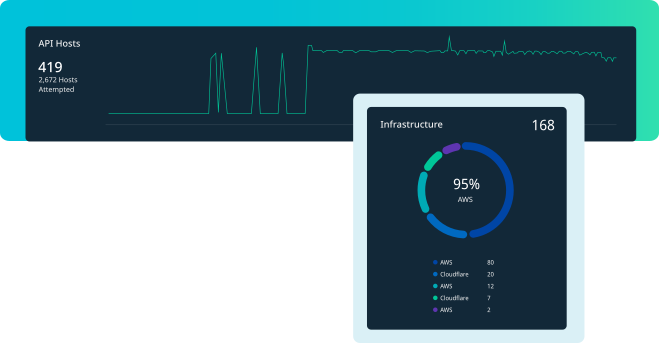
Runtime API Discovery
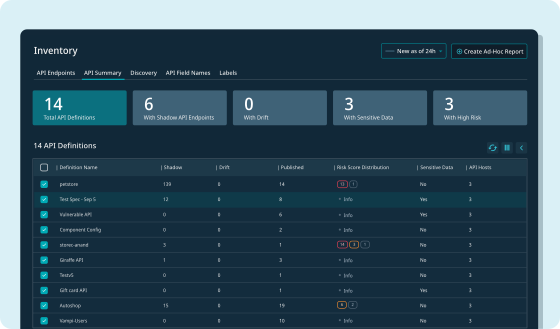
Automatically identifies all your API endpoints – documented, undocumented, third-party, and even shadow APIs to create a runtime API catalog.
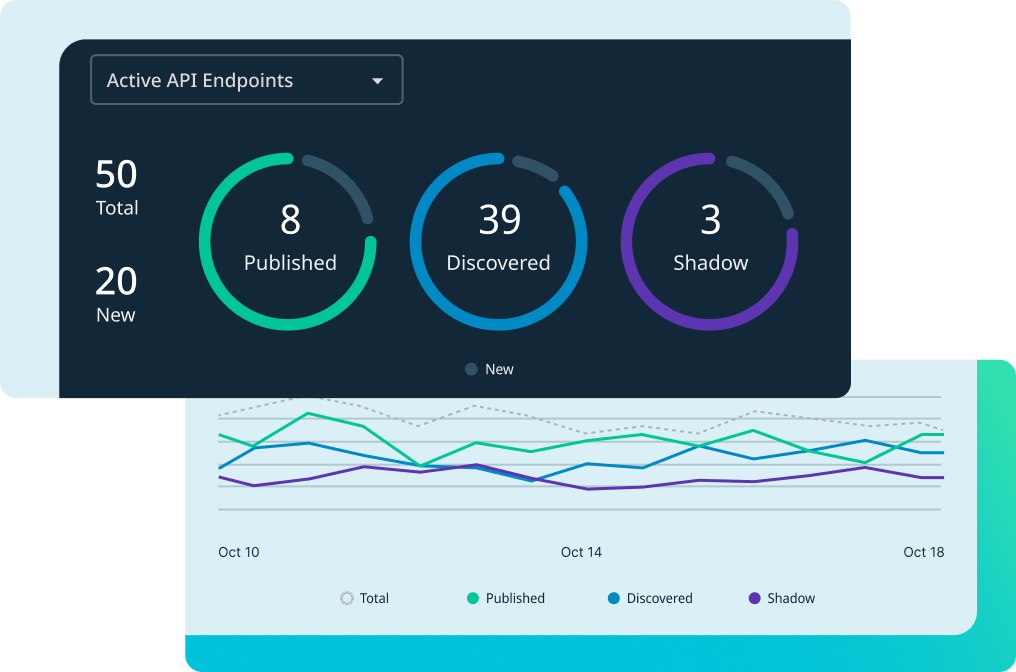
API Risk Prioritization
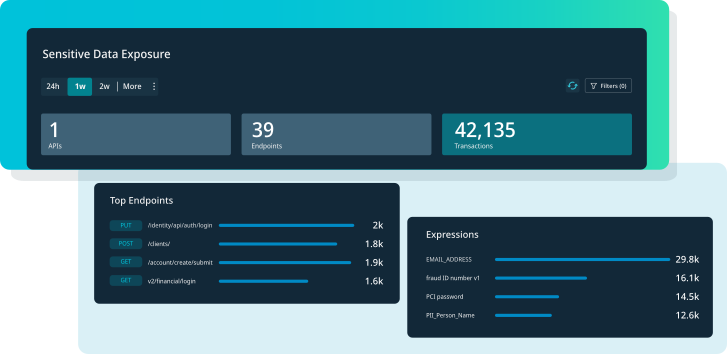
Discovered APIs are inventoried and assessed for risk related to access control, sensitive data leakage, and compliance with the published API specification.
Automatic API Spec Generation
If API specs are not available, Cequence can automatically create them, saving time and effort.
Real-Time Threat Prevention
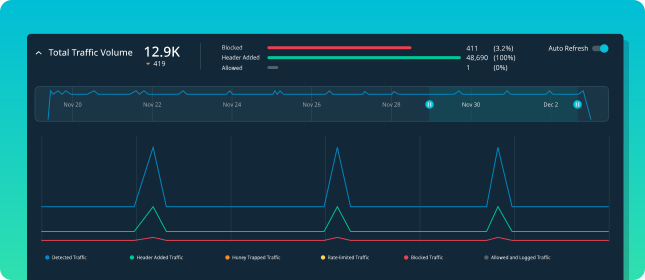
Cequence’s accurate bot detection allows organizations to block scraping bots with the confidence that legitimate traffic won’t be adversely affected.
Cequence’s comprehensive API discovery and inventory enables organizations to know what APIs are in use, where they are, and who has access to them.
What to Look for in API Discovery Tools
Most API discovery software can produce a list of endpoints. The difference between a list and an inventory your team can act on comes down to four questions.
- Does it find what nobody documented? Discovery that leans on specs or gateway configuration only confirms what you already knew. Real API discoverability means surfacing shadow and zombie APIs from live traffic, not from documentation.
- Does it show you the outside view? Your own telemetry cannot see hosts you forgot you owned. Attack surface discovery covers what an attacker finds before you do.
- Does it rank risk, or just count endpoints? An inventory of thousands of endpoints helps only if it tells you which ones to fix first, based on access control gaps, sensitive data and specification drift.
- Does discovery connect to enforcement? API discovery solutions that hand findings to a separate protection tool leave a window open between detection and response.
The Cequence Platform covers all four, so discovery and protection run on one system rather than two.
Additional Resources
Cequence Security application and API protection experts will show you how we can help you improve your security posture with a personalized demo. Nothing to deploy. All we need is your email.