
Cequence
API Security
API Security Posture Management, Testing, and Remediation
Cequence API Security is an AI-first solution that discovers, monitors, and tests your APIs, assessing a broad range of risks that can lead to compliance or governance issues, data loss, and business disruption.
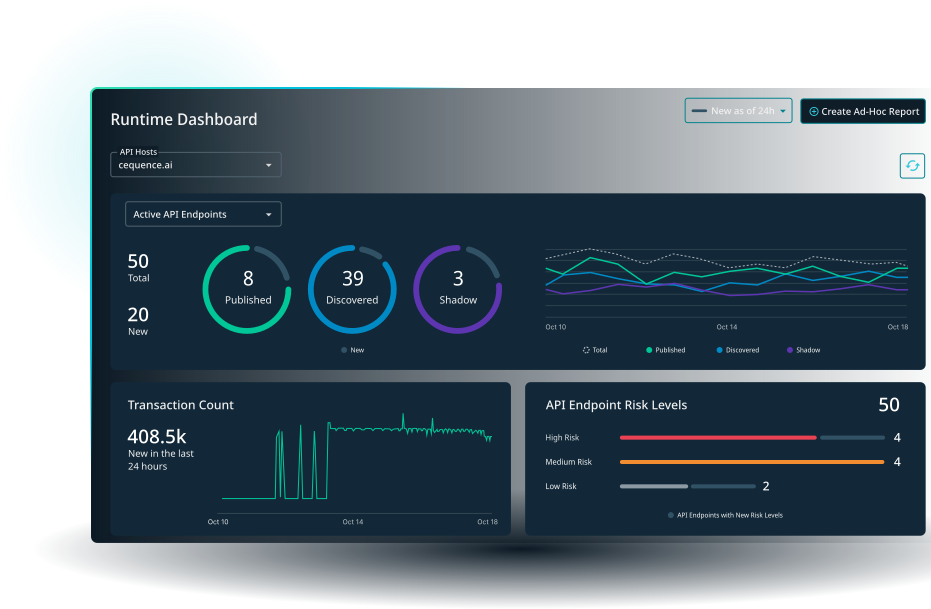
Today’s Businesses Run on APIs
IT, security, and development teams need visibility and control to enact a robust API security program. Use cases include:

API Discovery & Inventory

API Risk Identification & Classification

API Security Testing

Sensitive Data Detection, Masking, and Exposure Prevention

OWASP API Security Top 10 Risk Categorization
API Attack Surface Reduction
API Security Key Features
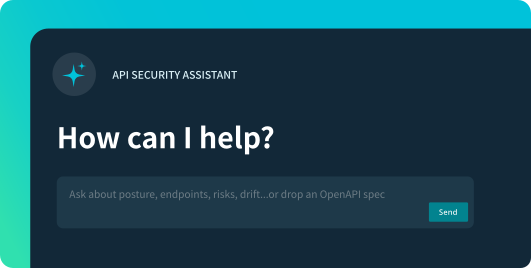
AI-First Architecture with Built-in AI Assistant and MCP Server
API Security’s built-in AI Assistant answers questions like “which public APIs handle sensitive data?” and returns ranked, evidence-backed findings teams act on in the same conversation. It also exposes every capability as MCP tools, so teams can use the product as part of their internal agentic workflows. Governance is built in; read actions run freely, while every write requires human-in-the-loop approval that shows the exact change first.
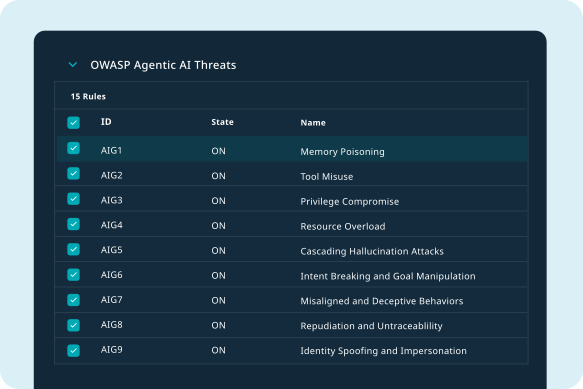
Compliance-ready Risk Rules and Reporting
API Security ships more than 200 pre-built risk rules mapped to 25 global frameworks, including every version of the OWASP API Security Top 10, PCI DSS, GDPR, HIPAA, SOC 2, ISO 27001, and NIST CSF. Audit-ready reports generate in a single click, building from live data, mapping findings to each framework’s controls, scoring risk by control area, and giving remediation guidance for every gap. Observe mode scores new rules without raising formal issues.
Comprehensive API Discovery and Inventory
Cequence discovers internal, external, and third-party APIs as well as edge, infrastructure, gateway, and hosting providers. A combination of inside-out and outside-in discovery provides attack surface and internal API visibility and inventory. Cequence integrates directly with your existing infrastructure such as API gateways or can be deployed inline.
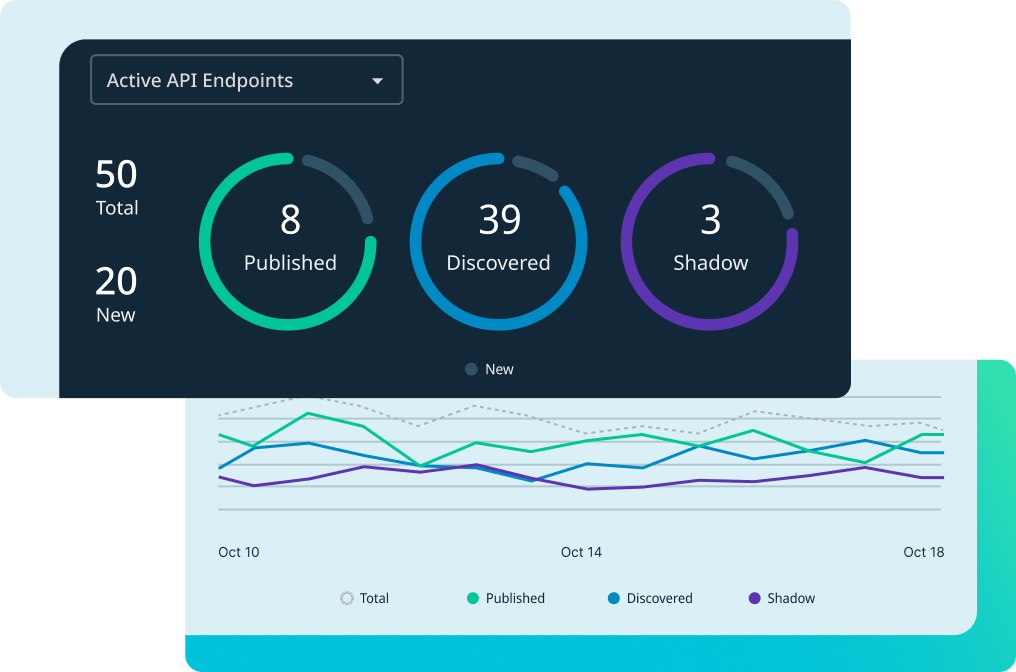
Continuous Risk Visibility
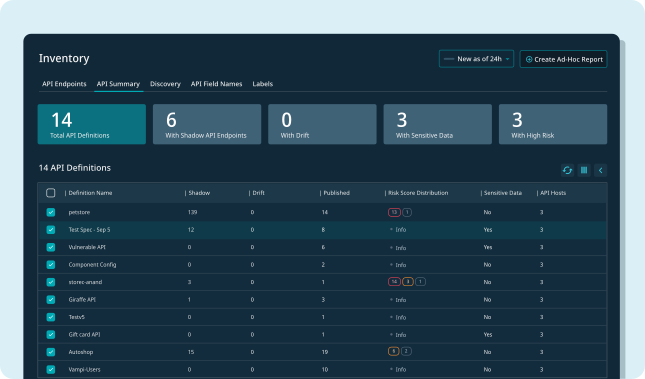
Cequence automatically identifies all your API endpoints – documented, undocumented, third-party, and even shadow APIs to create a runtime API catalog. Discovered APIs are inventoried and assessed for risk related to access control, sensitive data leakage, and even compliance with the published API specification – and automatically generate them if not available. Rules and prioritization are user configurable and require no coding or scripting.
Sensitive Data Exposure Prevention
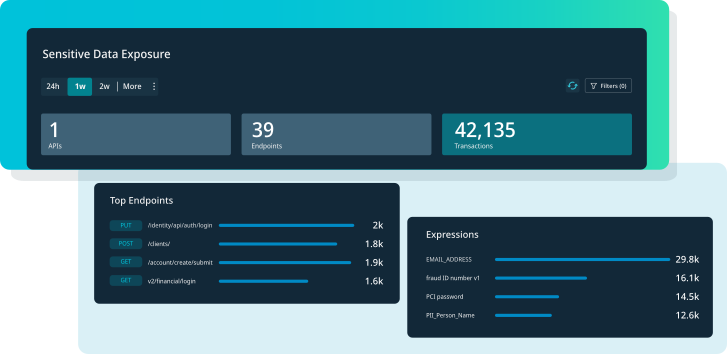
Cequence automatically identifies and masks sensitive data using ML-based rules with predefined (e.g., credit card numbers) and customizable data patterns. Sensitive data patterns are supported worldwide, enabling differentiation between a US driver’s license number from a Saudi National ID Card ID number, for example. Sensitive data is identified wherever it is, without having to explicitly define specific APIs that transact it or what data is sensitive.
Integrated API Security Testing
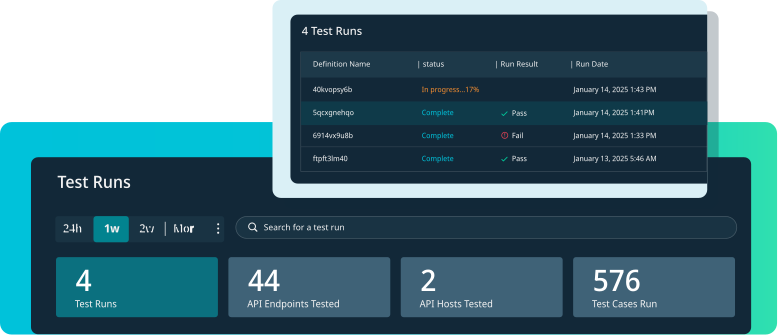
Cequence enables IT and development teams to thoroughly test their APIs, identifying and remediating vulnerabilities and coding errors, both in pre-production and at runtime. Test plans can be automatically generated from Postman collections or API specifications, eliminating a great deal of manual work. Supports CI/CD pipelines, IDEs, and stand-alone testing.
API Attack Protection
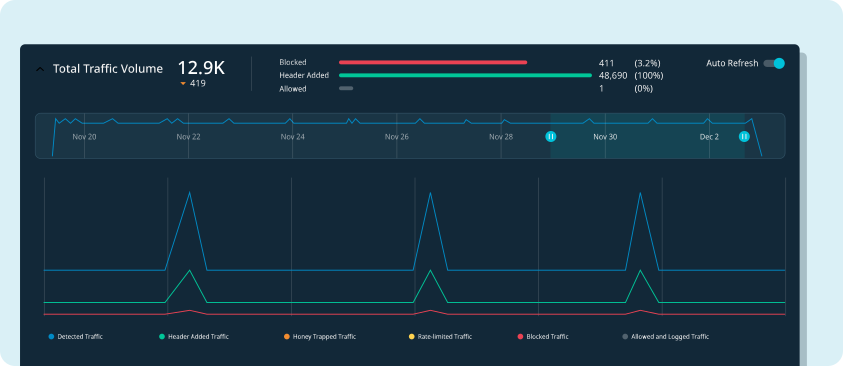
Cequence API Security protects web, mobile, and API applications from attacks to prevent data loss, theft, and fraud. ML-powered threat detection and analytics and integration with third-party defensive solutions such as WAFs and API gateways ensures protection against even the most sophisticated attacks. Cequence Bot Management provides native mitigation including blocking, logging, rate limiting, header injection, and deception.
Cequence API Security is Part of the Cequence Platform
Customer Success Story
Hibbett Scores with Cequence Security API Discovery, Compliance, and Protection
Cequence Security application and API protection experts will show you how we can help you improve your security posture with a personalized demo. Nothing to deploy. All we need is your email.