EMA Research –Only 33% of enterprises enforce AI agent least privilege access
Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.
BlogContact Us
Cequence Security
Financial Services
2023-predictions-staying-one-step-ahead-in-api-protection,api-security-2024-predictions,api-security-financial-services,api-security-lacking-for-ecosystem-and-third-party-apis,api-security-breaches,cfpb-announces-major-open-banking-proposed-rule,ffiec-api-security-guidance,financial-aggregators-a-vehicle-for-credential-exploitation,financial-services-api-protection,financial-services-customer-stops-millions-of-api-based-account-takeover-attacks-ato,guest-blog-api-security-off-to-a-booming-start-but-were-not-done-yet,reaching-a-tipping-point-in-identity-verification,regulations-and-standards-drive-need-for-api-security,revised-payment-services-directive-psd2,shield-right-while-shifting-left-to-eliminate-fdx-api-security-gaps-at-runtime,tales-from-the-front-lines-protecting-financial-services-mobile-application-apis-from-automated-attacks,the-open-banking-api-security-imperative,unpacking-the-new-cfpb-rule-on-open-banking
financial-services
Current Events
api-breach-duolingo,api-security-need-to-know-lessons-learned-from-the-peloton-security-incident,disney-account-takeovers-how-the-information-is-used-2
current-events
Industry Reports
api-layer-attacks-2026-dbir,best-in-class-api-security,dbir-api-security,new-api-threat-research-shows-that-shadow-apis-are-the-top-threat-vector,survey-highlights-api-business-value-and-api-security-balancing-act,verizon-2025-dbir-review,verizon-dbir-insights,when-does-comparison-shopping-become-malicious
industry-reports
OWASP
2023-predictions-staying-one-step-ahead-in-api-protection,api-breach-duolingo,api-protection-and-cloud-native-application-protection-platforms-cnapp,api-security-financial-services,api-security-meets-government-regulators,api-security-need-to-know-top-5-authentication-pitfalls,api-security101,api-security-breaches,cfpb-announces-major-open-banking-proposed-rule,connected-car-safety-and-api-security,evolution-of-owasp-api-top-10,owasp-api-risks-cant-be-blocked-but-can-be-fixed,owasp-api-vulnerabilities-exploited-to-bypass-api-security,tales-from-the-front-lines-how-third-party-apis-simplify-enumeration-attacks,top-7-selection-criteria-for-automated-bot-prevention-solutions,unpacking-the-new-cfpb-rule-on-open-banking,zero-trust-api-security-model
owasp
Product News
a-winning-trifecta-api-gateways-api-security-and-api-protection,advance-your-api-security-with-amazon-api-gateway-api-sentinel,ai-agent-prompt-injection-credential-theft,api-protection-in-heterogeneous-environments,application-security-in-kubernetes-why-we-joined-cncf,cequence-achieves-pci-dss-3-2-and-soc-2-compliance,cequence-end-of-year-product-recap-strengthening-your-api-security,cequence-security-awarded-best-enterprise-cybersecurity-solution-of-the-year,cequence-securitys-unified-api-protection-solution-wins-three-2023-globee-awards,cequence-unified-api-protection-wins-2023-cyber-top-20-award,cequence-api-security-and-hpe-greenlake,complete-api-security-coverage-with-proxy-and-service-mesh-integration,complete-api-security-with-cequence-uap-and-cdn-integrations,groundbreaking-api-security-generative-ai,sinet16-innovators-award-validates-api-security-and-bot-management-belong-together
cequence-product-news
CQ Prime Threat Research
a-defenders-view-of-log4j-in-automated-attacks,anatomy-of-a-retail-shopping-bot,api-security-need-to-know-excessive-data-exposure,api-threat-research-validates-robust-api-security,bot-as-a-service-the-consumerization-of-botting,cequence-blocks-credential-stuffing-attack,fake-account-creation-its-fraud-by-any-other-name,heres-why-javascript-based-bot-detection-doesnt-work-is-your-site-listed-here,hidden-dangers-of-untrusted-mcp-servers,how-this-cool-sneakerhead-mom-beat-the-bots,long4j,long4j-findings-confirm-log4j-vulnerability-patching-gaps,moving-from-threat-hunting-to-threat-catching,multi-tenant-saas-authentication-bypass-or-works-as-designed,network-iq-how-the-largest-api-threat-database-protects-your-apis,new-api-research-shows-62-growth-in-atos-targeting-login-apis,new-report-big-breaches-breed-bad-bots,reality-check-automated-shopping-bots-are-a-business-problem,romance-scams-plague-dating-apps,state-of-api-security-activity,the-api-security-conversation-that-the-verizon-data-breach-report-missed,what-are-api-keys-and-why-do-i-need-api-key-security
cq-prime-threat-research
About Cequence
3-steps-to-shielding-right-while-shifting-left-for-api-protection,agentic-ai-monetization,are-api-threat-protection-and-bot-management-related,cequence-achieves-aws-security-competency-status,cequence-announces-ml-based-security-enhancements,cequence-security-awarded-best-enterprise-cybersecurity-solution-of-the-year,cequence-security-named-a-2021-tag-cyber-distinguished-vendor,cequence-securitys-unified-api-protection-solution-wins-three-2023-globee-awards,cequence-unified-api-protection-wins-2023-cyber-top-20-award,cfpb-announces-major-open-banking-proposed-rule,comprehensive-api-protection,enabling-retail-deals-and-repelling-the-steals,ffiec-api-security-guidance,guest-blog-api-security-off-to-a-booming-start-but-were-not-done-yet,hand-sanitizer-samples-face-masks-and-api-security-an-rsa-2020-recap,industry-recognition-for-api-sentinel-kuppingercole,javascript-injection-good-for-fraud-detection-bad-for-security-2,making-a-build-vs-buy-bot-prevention-decision,organizations-are-changing-application-security-must-change-too,predictions-2021-getting-an-edge-against-the-bots,prep-the-halls-readying-your-retail-environment-for-the-holiday-rush,reaching-a-tipping-point-in-identity-verification,rsa-conference-2023-api-security,safeguarding-financial-health-why-cfos-should-prioritize-api-security,shield-right-while-shifting-left-to-eliminate-fdx-api-security-gaps-at-runtime,sinet16-innovators-award-validates-api-security-and-bot-management-belong-together,some-recent-api-security-related-gaffes-and-how-they-might-have-been-avoided,ten-things-your-api-security-solution-must-do-part-i,ten-things-your-api-security-solution-must-do-part-ii,the-analyst-perspective-observations-from-cequences-2021-api-specification-survey,unified-api-protection,unpacking-the-new-cfpb-rule-on-open-banking,what-happens-when-your-entire-company-learns-ai-together-we-found-out,why-do-i-need-api-security-if-i-have-a-waf-and-api-gateway,why-unified-api-protection
about-cequence
Customer Case Studies
api-security-case-study,application-security-solving-the-hardest-problem-first,balancing-bot-detection-with-customer-experience,cequence-unified-api-protection-squashes-phishing-campaign-in-a-matter-of-hours-time-to-value,customer-story-zoosk-security,financial-aggregators-a-vehicle-for-credential-exploitation,flash-sales-and-sneaker-drops,gift-card-and-loyalty-program-abuse,poshmark-api-protection-case-study,sms-pumping-fraud,tales-from-the-front-lines-protecting-financial-services-mobile-application-apis-from-automated-attacks,tales-from-the-front-lines-retail-customer-stops-200k-gift-card-fraud-scheme
customer-case-studies
API Security
2026-verizon-dbir-bots-web-app-attacks-agentic-ai,a-year-in-review-in-one-word-momentum,agentic-ai-application-protection-platform-waap,announcing-api-sentinel,announcing-cequence-waap,announcing-general-availability-of-cequence-api-sentinel-2-0,announcing-unified-api-protection-v2-0,api-layer-attacks-2026-dbir,api-security-api10-defined-as-bots-abusing-well-formed-apis,api-security-lacking-for-ecosystem-and-third-party-apis,api-security-need-to-know-lessons-learned-from-the-peloton-security-incident,api-security-threat-research-retail-holiday-report-2023,app-instrumentation,attack-detection-and-threat-hunting-common-topics,automating-attacks-with-chatgpt,better-bot-management,bola-attack-protection-telecom,business-logic-abuse,canadas-largest-retail-pizza-chain-moves-from-reactive-to-proactive-api-protection-with-cequence,cequence-achieves-pci-dss-3-2-and-soc-2-compliance,cequence-and-software-ag-partner-to-deliver-end-to-end-api-security,cequence-api-security-at-black-hat-2024,cequence-end-of-year-product-recap-strengthening-your-api-security,cequence-named-to-cyber-66-list,cequence-q4fy26-momentum-agentic-ai-security,cequence-security-makes-its-rsa-debut-2,cequence-unified-api-protection-squashes-phishing-campaign-in-a-matter-of-hours-time-to-value,cequence-api-security-and-hpe-greenlake,chatgpt-for-api-security,comprehensive-api-protection,discover-public-api-attack-surface-with-new-api-spyder,end-to-end-api-security,financial-services-api-protection,gartner-recognition-when-it-rains-it-pours,gift-card-and-loyalty-program-abuse,hey-api-what-you-token,how-a-broken-object-level-authorization-vulnerability-exposed-sensitive-data-api-security-report,how-automated-api-attacks-are-the-digital-equivalent-of-mockingbirds,how-bola-leads-to-enumeration-and-ato-attacks,idor-vulnerability,introducing-api-bites-from-cequence-security,iocs-in-your-apis,kasa-camera-vulnerability-discovery,leading-telecom-slashed-account-takeovers,looking-for-a-silver-tail-replacement,mergers-and-acquisitions-in-api-security-and-bot-management,new-api-threat-research-shows-that-shadow-apis-are-the-top-threat-vector,owasp-api-security-top-10-a-framework-for-improving-your-api-security-efforts,owasp-api-security-top-10-from-a-real-world-perspective,owasp-api-vulnerabilities-exploited-to-bypass-api-security,owasp-appsec-training-day-api-attacks-beyond-the-owasp-api-top-10,owasp-top-10-lists-end-state-or-starting-point,prying-eye-vulnerability-direct-to-api-enumeration-attack-enables-snooping,regulations-and-standards-drive-need-for-api-security,tales-from-the-front-lines-attackers-on-lockdown-focus-on-apis,tales-from-the-front-lines-attackers-target-apis-with-get-based-atos,tales-from-the-front-lines-protecting-financial-services-mobile-application-apis-from-automated-attacks,tales-from-the-frontlines-api-sentinel-drives-security-collaboration,the-cequence-security-blog-top-5-posts-of-2020,the-danger-of-web-scraping-and-how-to-prevent-it,ulta-beauty-reduces-costs-by-blocking-api-based-enumeration-attacks,unified-api-protection-7-3,unified-api-protection-for-telcos-customer-testimonial,unified-api-protection-recognized-kuppingercole,whats-new-cequence-api-security-platform-further-advances-end-to-end-vulnerability-and-automated-attack-mitigation,whats-new-cequence-unified-api-protection-siem-integration
api-security
Bot Management
2022-predictions-protecting-an-api-centric-world,2025-api-security-predictions,2026-verizon-dbir-bots-web-app-attacks-agentic-ai,a-defenders-view-of-log4j-in-automated-attacks,agentic-ai-api-security,agentic-ai-application-protection-platform-waap,agentic-ai-security-behavioral-analysis,ai-agents-are-bots-api-defense,analysis-preventing-fake-account-creation-and-romance-scams-2,announcing-cequence-waap,api-0day-response-a-moveit-story,api-breach-duolingo,api-layer-attacks-2026-dbir,api-protection-and-cloud-native-application-protection-platforms-cnapp,api-protection-in-heterogeneous-environments,api-protection-in-telecommunication-protected-in-less-than-30-minutes,api-security-2024-predictions,api-security-api10-defined-as-bots-abusing-well-formed-apis,api-security-in-your-operational-technology-ot,api-security-lacking-for-ecosystem-and-third-party-apis,api-security-podcast-how-apis-enable-digital-transformation-and-automated-attacks,api-security-threat-research-retail-holiday-report-2023,api-threat-detection,api-threat-prevention,api-threat-research-validates-robust-api-security,are-api-threat-protection-and-bot-management-related,are-these-13-scary-security-gaps-in-your-apis,automating-api-security,aws-vpc-traffic-mirroring-integration-coming-soon-2,beyond-magecart-understanding-the-risks-and-impacts-of-third-party-javascript,block-api-attacks,bot-attacks-one-week-in-the-life-of-a-customer,bulletproof-proxies-the-evolving-cybercriminal-infrastructure,bulletproof-proxy-market-update,business-impacts-of-api-security-breaches,canadas-largest-retail-pizza-chain-moves-from-reactive-to-proactive-api-protection-with-cequence,cequence-security-awarded-best-enterprise-cybersecurity-solution-of-the-year,cequence-securitys-unified-api-protection-solution-wins-three-2023-globee-awards,cequence-unified-api-protection-wins-2023-cyber-top-20-award,creating-credential-stuffing-resistant-applications,dbir-api-security,disney-account-takeovers-how-the-information-is-used-2,ffiec-api-security-guidance,financial-services-api-protection,forrester-bot-management-wave-2022,fortune-500-retailer-saves-1-7-million-by-eliminating-account-take-overs-2,heres-why-online-holiday-inventory-is-often-gone-before-you-get-there-3,how-shadow-apis-simplify-automated-attacks,implementing-a-dynamic-sampling-strategy-in-spark-streaming,industry-recognition-for-runtime-application-security-omdia-research,introducing-cq-prime-the-cequence-security-threat-research-team,moving-fast-without-api-guardrails,old-habits-die-hard-industrial-controls-credential-sharing-and-password-spraying,pci-dss-4-compliance-api-security,poshmark-api-protection-case-study,rsocks-takedown,simplifying-bot-prevention-with-cdn-integration,sinet16-innovators-award-validates-api-security-and-bot-management-belong-together,state-of-api-security-activity,survey-highlights-api-business-value-and-api-security-balancing-act,tales-from-the-front-lines-a-long-weekend-ruined-for-whom-2,tales-from-the-front-lines-attackers-on-lockdown-focus-on-apis,tales-from-the-front-lines-attackers-target-apis-with-get-based-atos,tales-from-the-front-lines-how-third-party-apis-simplify-enumeration-attacks,tales-from-the-front-lines-large-retailer-achieves-near-immediate-time-to-value,tales-from-the-front-lines-maintaining-detection-efficacy-and-your-cool-in-the-summer-heat,tales-from-the-front-lines-protected-in-just-33-minutes,tales-from-the-front-lines-retailer-prepares-for-holiday-bot-battle-in-a-matter-of-weeks,tales-from-the-front-lines-why-simple-attacks-like-content-scraping-are-the-hardest-to-block,tales-from-the-frontlines-increasingly-sophisticated-cat-and-mouse-games,ten-things-your-api-security-solution-must-do-part-ii,the-critical-role-real-time-protection-plays-in-api-security,the-rise-fall-of-single-request-bots-2,threat-advisory-recent-high-volume-bot-traffic-from-ipvanish-vpn-against-retailers,unified-api-protection,unified-api-protection-7-3,using-an-api-security-checklist-what-should-you-look-for,verifiable-ai-agent-identification,verizon-dbir-insights,what-are-fake-accounts-and-how-can-they-be-worth-44-billion,what-is-account-takeover-ato,what-is-api-threat-detection,what-is-api-threat-mitigation,what-sets-cequence-apart-from-anyone-else,why-unified-api-protection,your-bot-problem-may-be-an-api-problem
bot-management
AI
2026-verizon-dbir-bots-web-app-attacks-agentic-ai,agentic-ai-api-security,agentic-ai-monetization,agentic-commerce-bot-defense,ai-gateway-introduction,automating-attacks-with-chatgpt,beyond-captcha-biometric-verification-bot-detection,bot-defense-pricing-success-penalty,chatgpt-for-api-security,the-genai-gold-rush
ai

Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.

FEATURED BLOG

AI Security Blog

Introducing Agent Trust: Managing Agents with Identity Plus Behavior

AI agent identity verification proves who an agent is. Agent Trust adds behavioral analysis so security teams can govern what it does.
Read More
Introducing Agent Trust: Managing Agents with Identity Plus Behavior
Magecart vulnerability
CQ Prime Threat Research

Beyond Magecart: Understanding the Risks and Impacts of Third-Party JavaScript

February 14, 2020

6

Read Blog
Third-party JavaScript is a common technique used to add functionality, user experiences, or security paradigms to your web site. However, these website additions can introduce significant friction. Not all users want to wait for the various JavaScript components to load, and no one is interested in losing their credit card info to Magecart-related content skimming. […]
Building and automobile representing Industrial Control Systems security
CQ Prime Threat Research

Old Habits Die Hard: Industrial Controls, Credential Sharing and Password Spraying

January 15, 2020

6

Read Blog
For years, the security implications related to Industrial Control Systems, SCADA and Industrial Internet of Things have been treated as a low(er) priority because these systems were closed, embedded deep in the shop floor, and had minimal network connectivity. Today, these systems have network connectivity, and are accessible from the web, but the security stance […]
single request bots
CQ Prime Threat Research

The Rise & Fall of Single Request Bots

December 19, 2019

6

Read Blog
The cat and mouse game between bot operators executing automated attacks and prevention vendors has become increasingly sophisticated, with each side applying more intelligence to their respective prevention or malicious efforts. Prevention vendors collect increasingly sophisticated telemetry while bot operators reverse engineer to fully understand the detection techniques, creating single request bots that blend in […]
Disney+ Attack - Account Takeover
CQ Prime Threat Research

Disney+ Account Takeovers: How the Information is Used

November 20, 2019

4

Read Blog
I recently joined Cequence as a Hacker in Residence and am excited to focus on the world of automated attacks and how BOTs are used for things like account take over and credential stuffing attacks. The research into the attacks and customer stories are incredibly intresting. When I heard that roughly 10 million accounts were created on […]
Protecting financial services apis
Bot Management

Tales from the Front Lines: Protecting Financial Services Mobile Application APIs From Automated Attacks

November 12, 2019

3

Read Blog
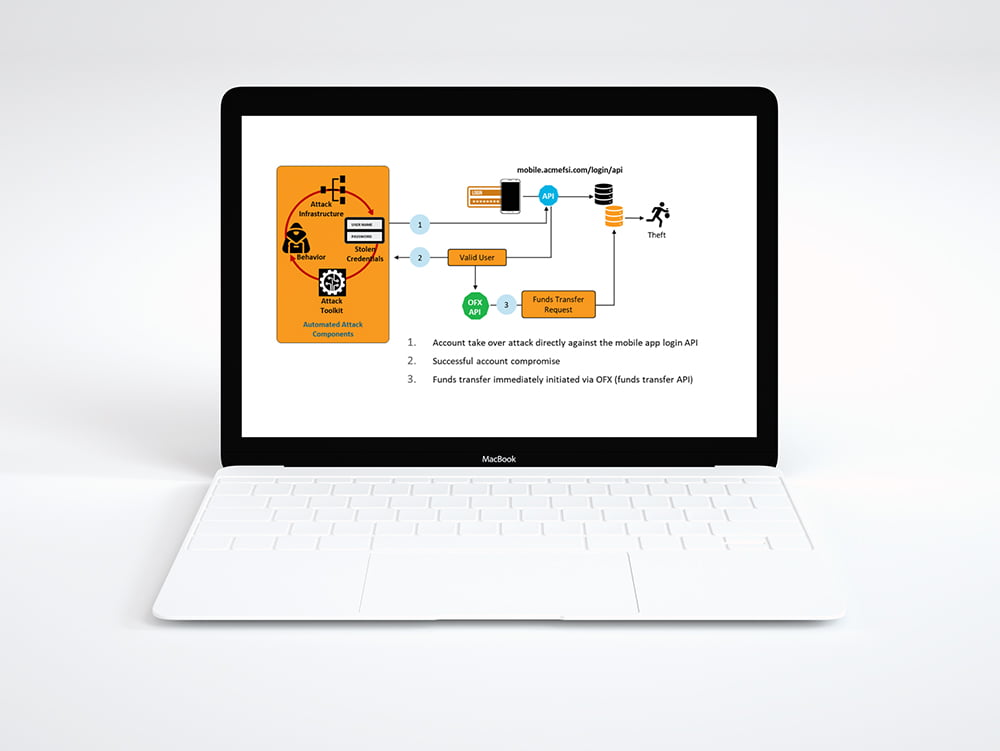
Next week we will be at FS-ISAC in Washington DC (booth #60) to present (Monday, Nov. 18, 4:15PM-5:00PM) and talk with financial services organizations about how we can help them prevent fraud and theft that may result from automated account takeover attacks against their mobile and API-based applications. It’s no secret that financial services organizations […]
protecting from automated attack
Customer Case Studies

Tales from the Front Lines: A Long Weekend Ruined for Whom?

November 5, 2019

6

Read Blog
Automated bot attacks are a bit different than other types of cyber-attacks in several ways. First, these attacks are difficult to defend against because they appear to be legitimate uses of the public-facing application business logic (e.g., login, account sign up, browse, shop, check out, etc.), and blocking the seemingly real traffic without due cause […]
Holiday Inventory
CQ Prime Threat Research

Here’s Why Online Holiday Inventory is Often Gone Before You Get There

October 24, 2019

5

Read Blog
As the holidays draw nearer and consumers begin frequenting their favorite online retailers in search of the perfect gift, it seems an appropriate time to put the spotlight on a topic that gives shoppers heartburn as they search online: shopping bots that automatically buy up all inventory. For example, it could be the latest Nike […]
API Security
API Security

API Security Podcast: How APIs Enable Digital Transformation and Automated Attacks

October 18, 2019

2

Read Blog
It’s no secret that APIs are an invaluable tool for application developers who are tasked with doing more with less. Driven by mobile device ubiquity and the move towards modular applications where APIs are used as the foundational elements of the application business logic, organizations are using APIs for many things, including to facilitate interoperation […]
zoosk
Bot Management

How Zoosk Detects and Mitigates Malicious Bots

October 15, 2019

4

Read Blog
A leader in online dating, Zoosk is committed to delivering personalized matches to its 35+ million members. With the ultimate goal of creating lasting and meaningful relationships, protecting their users from fraud that may be caused by automated bots is a top priority for the Zoosk security team. Finding Love and Romance – Securely and […]
Prying-Eye Vulnerability
CQ Prime Threat Research

Prying-Eye Vulnerability: Direct-to-API Enumeration Attack Enables Snooping

October 1, 2019

4

Read Blog
The Prying-Eye vulnerability is an example of an enumeration attack that targets web conferencing APIs with a bot that cycles through (enumerates) and discovers valid numeric meeting IDs. If the common user practice of disabling security functionality or not assigning a password is followed, then the bad actor would be able to view or listen […]
Romance Scams
Customer Case Studies

Analysis: Preventing Fake Account Creation and Romance Scams

September 4, 2019

4

Read Blog
Average Theft Prevented Per Romance Scam: $12,000 Credentials represent one of the Four Pillars of Detection that the CQ Prime Research Team uses to help our customers understand and ultimately prevent automated bots and the associated fraud. It’s common knowledge that credentials are used to create fake accounts in an automated manner to achieve fraudulent […]
cq-prime automated bot attacks - attack research
CQ Prime Threat Research

Introducing CQ Prime–the Cequence Security Threat Research Team

July 31, 2019

5

Read Blog
I’d like to introduce you to CQ Prime, the Cequence Security threat research team whose singular mission is to help the security industry and our customers understand the Tactics, Techniques and Procedures (TTPs) utilized by cybercriminals who execute automated malicious bot attacks against your public facing web, mobile, API-based applications. These attacks target your application […]
Bulletproof Proxies
CQ Prime Threat Research

Bulletproof Proxies: The Evolving Cybercriminal Infrastructure

July 31, 2019

4

Read Blog
What is Bulletproof Hosting? The concept of Bulletproof Hosting is relatively well known in the security universe. These services allow customers to upload and distribute malware, illegal pornography, manage phishing sites, and host other well-known security threats. From the perspective of an attacker, a good Bulletproof Hosting service will: Provide anonymity and protection from prying […]
Eliminating Account Take Overs
Customer Case Studies

Fortune 500 Retailer Saves $1.7 Million by Eliminating Account Take Overs

July 18, 2019

2

Read Blog
The retail industry is commonly targeted by bad actors who use stolen credentials and automated bots to launch high volume account take over attacks that result in financial losses through theft and fraud, as well as damage to the brand. The ‘2018 Cost of Retail Fraud’ report published by LexisNexis states that every $1.00 lost […]
AWS VPC Traffic Mirroring
Product News

AWS VPC Traffic Mirroring Integration Coming Soon

July 17, 2019

3

Read Blog
Back to work after the AWS re:Inforce conference in Boston and the July 4th weekend and I am super pumped about what I learned at AWS re:Inforce. Having attended a couple of AWS re:Invent conferences, which have become ginormous, it was refreshing to attend a security-focused AWS conference. It was a great opportunity to network […]
Dynamic Sampling
Product News

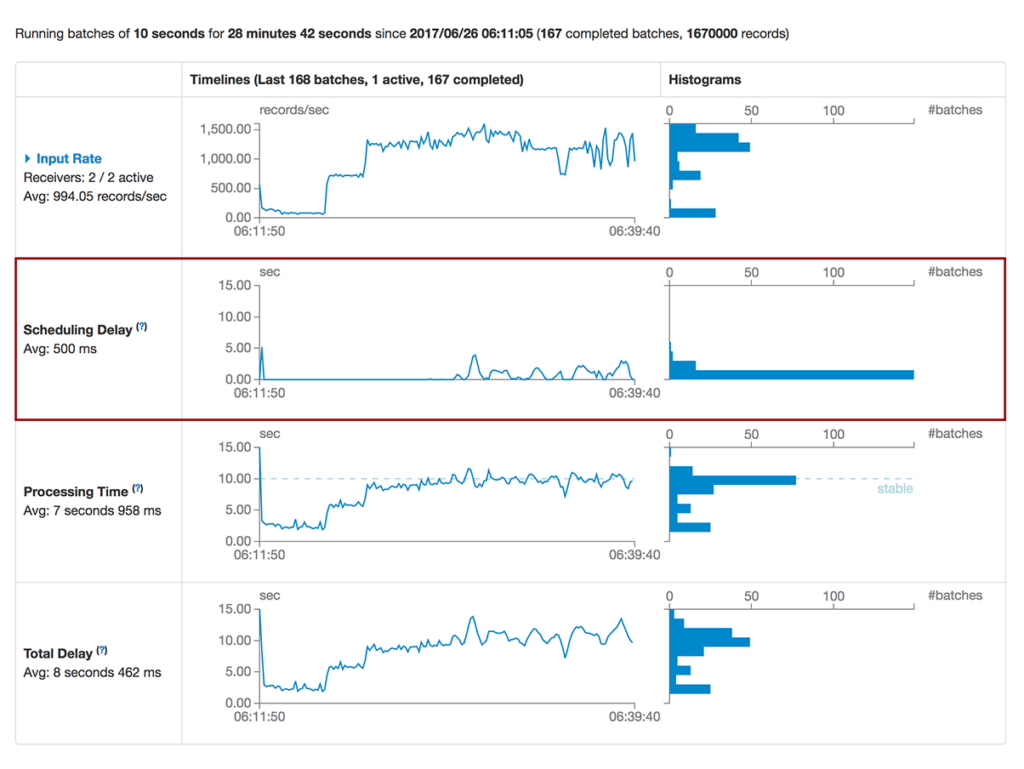
Implementing a Dynamic Sampling Strategy in Spark Streaming

July 16, 2019

8

Read Blog
We began using Apache Spark in 2015 as an integral component of our underlying data processing infrastructure. We chose to use it for the following reasons: It’s a single platform that allows us to implement both real-time streaming as well as offline batch processing. Both are critical elements in our architecture. It provides excellent support […]
Fake Account Creation
Bot Management

Fake Account Creation: It’s Fraud by Any Other Name

July 1, 2019

4

Read Blog
Early use cases of fake account creation were to anonymously request info, avoid spam from an online merchant or participate anonymously in a conversation. Today, with so much of our lives managed behind rich, account-based application platforms, fake account creation abuse is commonplace and more often than not, used to execute a secondary attack such […]
business logic abuse - app firewall
Bot Management

Application Security – Solving the Hardest Problem First

June 5, 2019

5

Read Blog
Today we announced Cequence App Firewall, the second security module for our Application Security Platform that leverages CQAI, our patented AI-powered analytics engine, to prevent data loss and compromise brought on by vulnerabilities exposed in your web, mobile, API-based applications. App Firewall is not a WAF in the traditional sense. Yes, it has the necessary […]
bot defense - prevent business logic abuse
About Cequence

What Sets Cequence Apart from Anyone Else

May 20, 2019

9

Read Blog
Cequence Security prevents business logic abuse with our AI-based Application Security Platform that discovers all of your public facing web, mobile and API-based applications, then detects any malicious transactions targeting those applications, allowing you to then apply policies to prevent the attack. As co-founder and CTO, I wanted to take a moment to highlight what […]
WAF security
About Cequence

WAFs Are Failing To Protect Hyper-Connected Organizations. But Help Is On Its Way

May 14, 2019

3

Read Blog
Over the last 10 years, we’ve seen the continuing growth and evolution of hyper-connected organizations. These are the forward-leaning enterprises that have embraced the Internet to connect customers, partners, and suppliers, enabling them to adopt digitally-driven business models that can eliminate boundaries and accelerate growth. One of the key enablers of hyper-connected organizations are the […]
Kubernetes Security
About Cequence

Application Security in Kubernetes: Why We Joined CNCF

April 9, 2019

5

Read Blog
We recently joined CNCF for two specific purposes. First off, our application is a distributed, containerized architecture that runs in a Kubernetes environment and as such, we want to support the project as a whole. The second reason we joined is to help educate customers on ways in which Kubernetes security can be embedded into […]
application security
Bot Management

Organizations Are Changing, Application Security Must Change Too

March 21, 2019

4

Read Blog
RSA Conference, arguably the biggest security conference in the world, recently finished in San Francisco. As I reflect back on my conversations at the conference with security practitioners from a broad range of industries, I realize that there are certain trends that these organizations are dealing with – and looking to vendors for help. It’s […]
rsa debut 2019
About Cequence

Cequence Security Makes Its RSA Debut

March 12, 2019

2

Read Blog
After a busy week sharing our news of $17M in Series B funding with the media, we followed that with a week of non-stop craziness at RSA 2019. And it was a good one. We locked down prime real estate in the Early Stage Expo and spent 3 days discussing application security challenges – and […]
Bot Attacks customer insights
Customer Case Studies

Bot Attacks – One Week in the Life of a Customer

December 20, 2018

2

Read Blog
Each week, we provide our customers with a detailed report on malicious bot attacks targeting their organizations with the intent of gaining unauthorized access to the critical applications that connect their digital ecosystems. Because the Cequence API Spartan solution protects all targeted channels–web and mobile apps, as well as strategically important API services–we’re able to […]
data breach - bot attack
Bot Management

New Report: Big Breaches Breed Bad Bots

December 8, 2018

2

Read Blog
By now we’ve all seen the news on the recent Marriott breach. Yup, it was a big one. But there have been many other significant breaches in 2018, including Facebook, Quora, Panera, and the list goes on. Those breaches grab the headlines for just a few days, but they have a long tail that continues […]
working at Cequence Security
About Cequence

Working at Cequence Security

November 10, 2018

3

Read Blog
Prospective employees frequently inquire about our company culture at Cequence Security, so I thought I would share my thoughts on the topic. Before I do that, it makes sense to define mission and culture, as those two topics go hand in hand. A mission declares an organization’s purpose, or why it exists, while the company […]
balance-bot-detection
Bot Management

Balancing Bot Detection With Customer Experience

November 10, 2018

4

Read Blog
This past weekend, I needed to book my travel for an upcoming business trip. When I went to purchase my plane ticket, I found myself unable to login to my account. Instead, I encountered an ‘Access Denied’ message. I’ve traveled extensively with this airline for a while, enough to earn elite status in their rewards […]
JavaScript Injection
Bot Management

JavaScript Injection: Good for Fraud Detection. Bad for Security

November 3, 2018

5

Read Blog
The wide availability of attack components on the dark and public web makes it easy even for novice cybercriminals to conduct a successful attack on a website, API, or mobile application. With automated, ‘bot’ traffic quickly eclipsing legitimate user activity at some organizations, IT security teams, along with fraud teams, are keen to implement defenses […]
Illustration representing the identity verification challenges facing security and fraud teams.
Bot Management

Reaching a Tipping Point in Identity Verification?

October 20, 2018

5

Read Blog
As security professionals, we have a bit of a reputation for melodrama. A breach happens, we make a lot of fuss for a few weeks, and then we quickly move on to the next topic dominating our news cycles. Even when a breach seems pretty dire to a particular company and its customers, it’s usually […]
Financial Aggregators
Bot Management

Financial Aggregators a Vehicle for Credential Exploitation?

October 20, 2018

7

Read Blog
One of the first issues we tackled for customers was detecting and mitigating automated (i.e. “bot) attacks against web applications. As an ex-CISO who struggled with these attacks, I wanted us to build tools that would focus on that initial problem. Since then, we have expanded our product roadmap significantly and increased our scope to help […]

Get an Attacker’s View
into Your Organization


Schedule A Demo